Latest Cybersecurity News
View all →
GitHub App keys can still enable takeovers long after they are forgotten
“It is possibly an intentional design trade-off, not an oversight,” Sarkar said, commenting on the implementation of short-lived tokens alongside a permanent key. “This is…
The Infrastructure Already Has Eyes. We Need to Teach Them What to See.
Industrial cybersecurity has spent years getting better at seeing what is happening inside networks. We have more asset discovery, monitoring, segmentation, vulnerability management and detection…
Supporting ASD’s multi-factor authentication campaign: Why MFA matters more than ever
The Australian Signals Directorate (ASD) has this month issued a clear call to action through its Multi-factor authentication: Switch it on campaign, urging businesses, organisations,…
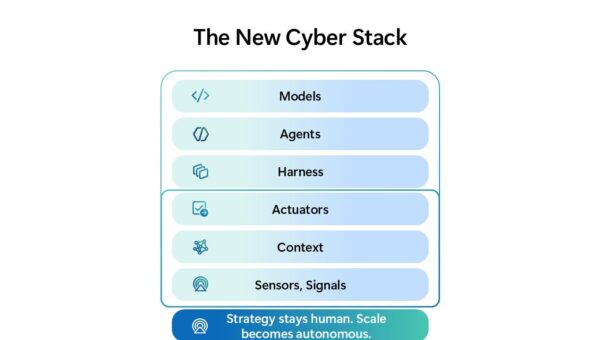
Reimagining the SOC for the agentic era in Microsoft Defender
The physics of cybersecurity are changing. So must the security operations center (SOC). Cyberattackers are using agents to automate execution at unprecedented scale. What once…
Behind the scenes: The making of a Global Threat Report
The first Elastic Global Threat Report was published earlier this week. In it, you will learn about trends observed by our threat researchers, our predictions…
Hackers start exploiting critical WordPress flaw for code execution
Threat actors have moved from probing WordPress sites vulnerable to CVE-2026-87902 to exploiting the flaw to write files to disk that execute shell commands when…
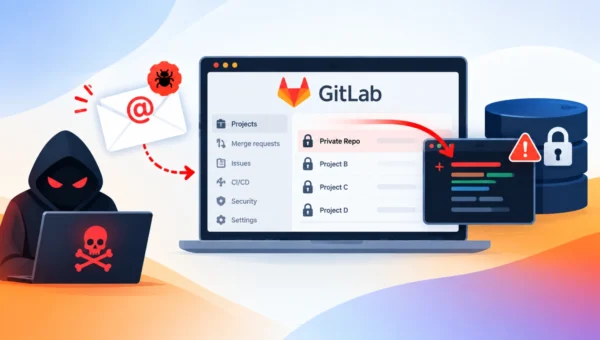
GitLab Email Feature Vulnerability Lets Attackers Push Code Into Private Repositories
GitLab’s “Email work item to this project” feature can become a repository-compromise primitive when its private address is exposed, according to research published by Aikido…
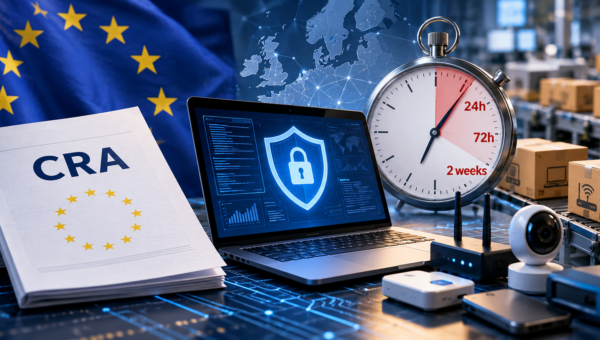
CRA Reporting Is Live: What Manufacturers, Vendors, and Distributors Need to Know
By Matthew Brady, Senior Security Engineering Manager, Black Duck As of September 11, 2026, Article 14 of the EU Cyber Resilience Act (CRA) is in…
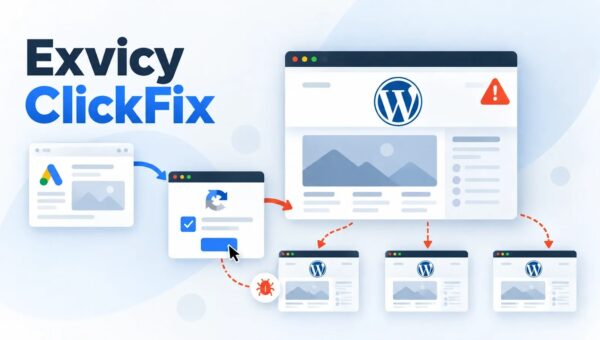
Exvicy ClickFix Malware-as-a-Service Copies ErrTraffic to Hijack WordPress Sites
A new Malware-as-a-Service platform, Exvicy, is actively abusing compromised WordPress websites to deliver ClickFix lures disguised as Cloudflare Turnstile verification pages. Researchers at Sekoia assess…