15,200 OpenClaw Control Panels Exposed Online with Full System Access
A critical security oversight has left thousands of AI agents wide open to the public internet. 15,200 instances of the OpenClaw AI framework (formerly Clawdbot…
A critical security oversight has left thousands of AI agents wide open to the public internet. 15,200 instances of the OpenClaw AI framework (formerly Clawdbot…
Fancy Bear has launched a sophisticated campaign exploiting a critical zero-day vulnerability in Microsoft RTF files to target users across Central and Eastern Europe. The…
“Chat & Ask AI,” a highly popular mobile application available on both Google Play and the Apple App Store, has suffered a significant data exposure.…
The latest campaign, they have switched to misusing a legitimate remote administration tool called NetSupport RAT. A cybercriminal group known as “Stan Ghouls” (or Bloody…
A massive, eleven-month campaign to root out sophisticated attackers from the nation’s critical infrastructure. The Cyber Security Agency of Singapore (CSA) and the Infocomm Media…
A sophisticated new cyber campaign has been detected targeting Ivanti Endpoint Manager Mobile (EPMM) systems. Starting on February 4, 2026, threat actors began exploiting two…
A new wave of identity fraud has hit the remote job market, with North Korean (DPRK) operatives adopting a sophisticated new tactic to bypass hiring…
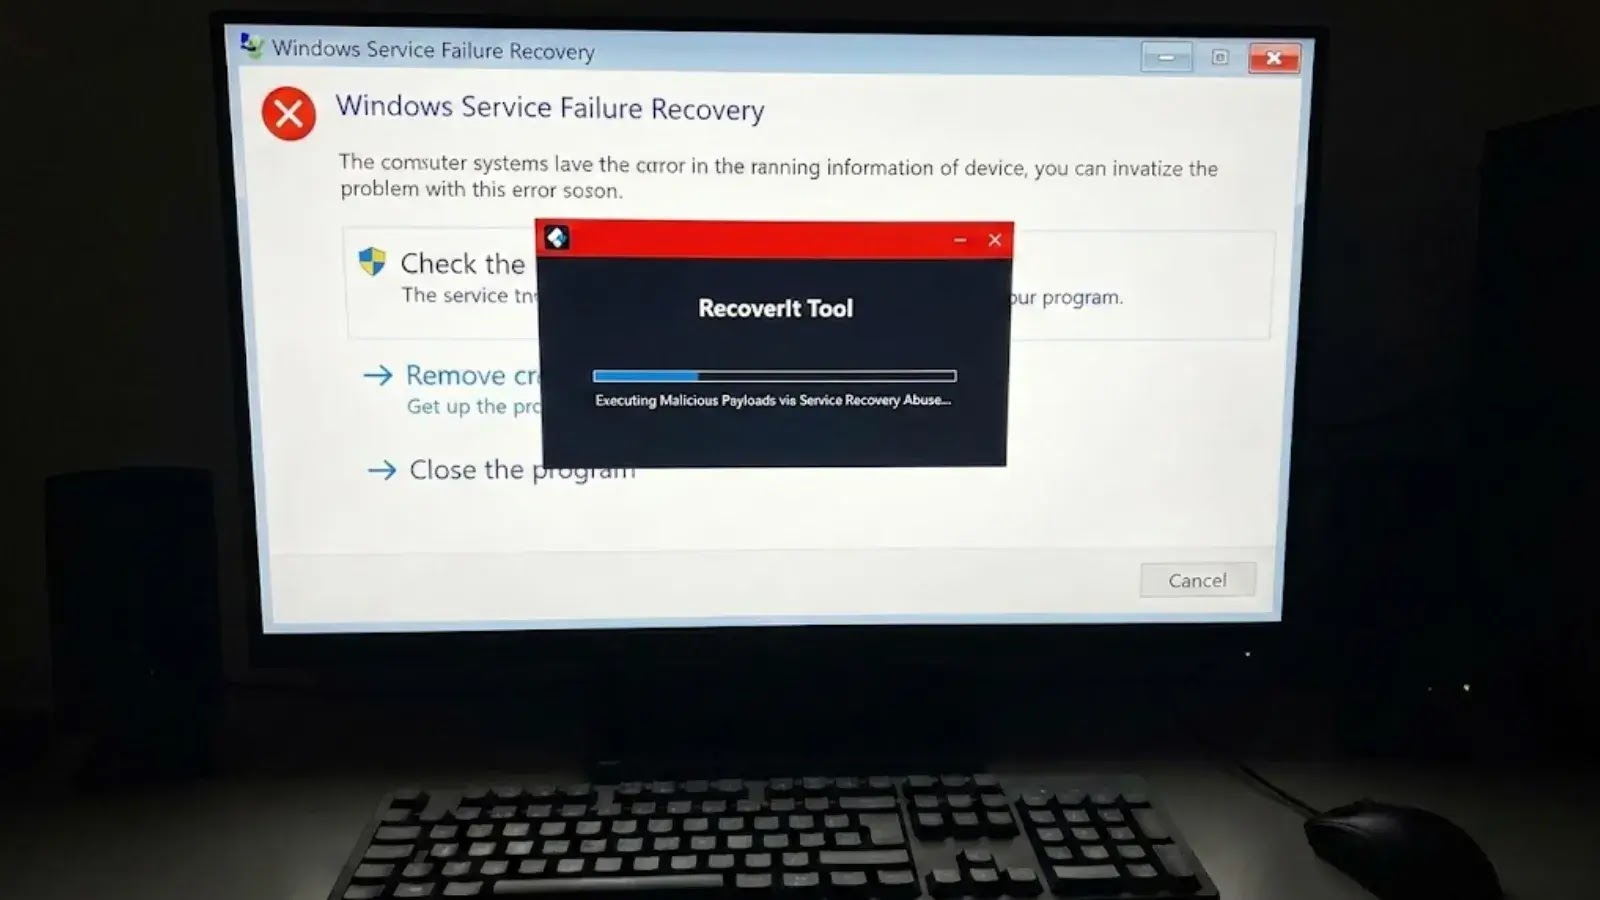
A new offensive security tool named “RecoverIt” has been released, offering red teamers a stealthy method for lateral movement and persistence by abusing the Windows…
A new evolution in ClawHub skill-based attacks that effectively sidesteps recent security measures. Rather than embedding base64-encoded payloads directly in SKILL.md files, threat actors have…
The North Korean-backed advanced persistent threat (APT) group known as ScarCruft has significantly evolved its attack techniques. In a departure from their established methods, the…
Threat actors are actively exploiting critical vulnerabilities in SolarWinds Web Help Desk (WHD) to deploy custom malware and establish persistent remote control. Security researchers observed…
A new, sophisticated malware campaign dubbed “LTX Stealer.” This malware represents a shift in attacker techniques, utilizing legitimate software frameworks and cloud services to hide…