DarkSword Server Combines iPhone Exploits With Fake Apple ID Login Page
DarkSword’s leaked iOS exploit chain is now powering a fast‑moving server cluster that marries one‑click Safari exploitation with a convincing fake Apple ID login page,…
DarkSword’s leaked iOS exploit chain is now powering a fast‑moving server cluster that marries one‑click Safari exploitation with a convincing fake Apple ID login page,…
Six newly disclosed vulnerabilities in Flowise, a popular open‑source platform for building AI agents and LLM workflows, allow unauthenticated and low‑privileged attackers to achieve remote…
A critical vulnerability in Gitea has been identified, potentially allowing unauthenticated remote attackers to read arbitrary files on vulnerable servers and escalate to remote code…
Security researchers have revealed a series of attacks that could enable malware on a compromised Windows device to hijack accounts protected by Google-synced passkeys. This…
A new Metasploit Framework module has been submitted for review, targeting the critical Ruby on Rails Active Storage vulnerability, tracked as CVE-2026-66066. This submission poses…
North Korea’s national antivirus appears to have quietly pivoted to ClamAV’s open‑source engine, recompiled it, and shipped it under four different domestic product names underscoring…
TP-Link has announced a high-severity security vulnerability in its TL-WR940N v6 wireless router that could allow an unauthenticated remote attacker to execute arbitrary code and…
N-able has issued an urgent hotfix to address a critical authentication-bypass vulnerability in its N-central remote monitoring and management (RMM) platform, following confirmation of active…
XCSSET v40 marks a significant escalation in macOS-focused supply chain attacks, weaponizing poisoned Xcode projects to hijack Chrome and Trojanize Telegram while operating almost entirely…
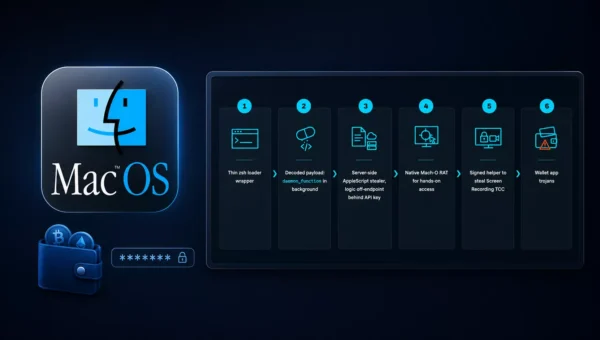
A newly disclosed macOS malware campaign dubbed MacSync weaponizes fake Claude AI installation guides to deploy a six-stage stealer and remote access trojan. Documented by…
HackerOne has rolled out a significant policy change requiring all hackers to complete identity verification before submitting reports to Bug Bounty Programs (BBPs). The update,…
The double-extortion ransomware group CRPx0 has listed Hyundai’s Turkish operations on its dark web leak site, claiming to have exfiltrated 1.5 GB of sensitive personnel…