Critical MLflow SSRF Flaw Exploited in the Wild
A critical unauthenticated server-side request forgery (SSRF) vulnerability in MLflow, tracked as CVE-2026-64849, is being actively exploited within hours of its disclosure, according to watchTowr.…
A critical unauthenticated server-side request forgery (SSRF) vulnerability in MLflow, tracked as CVE-2026-64849, is being actively exploited within hours of its disclosure, according to watchTowr.…
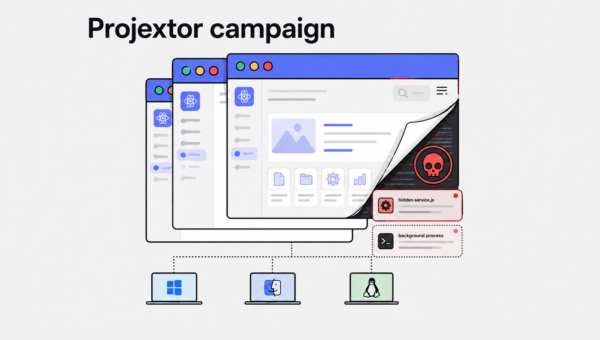
Threat actors behind the Projextor campaign are abusing Electron-based productivity applications to conceal malware-like capabilities behind fully functioning document converters, meal planners, recipe tools, and…
Apple has released security updates for iPhones, iPads, and Macs to address 28 vulnerabilities across its latest operating systems. These updates, issued on August 17,…
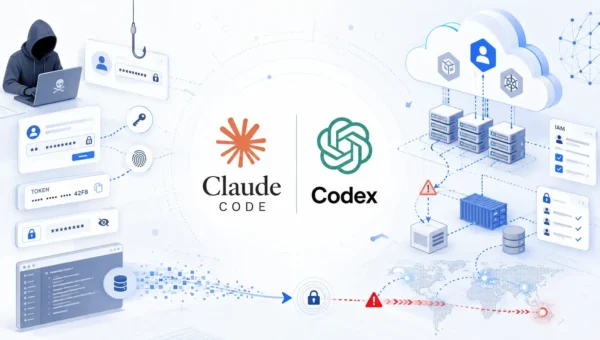
Threat actors are increasingly using coding assistants as operational tools. Detailed research from Gambit Security highlights three campaigns where Claude Code, OpenAI Codex, and large…
A targeted cryptocurrency intrusion has exposed how Google-hosted Apps Script pages can be weaponized to profile prospective victims before delivering signed Windows malware. The campaign…
HoneyMyte, the China-aligned espionage group also tracked as Mustang Panda, has upgraded its CoolClient backdoor with a signed Windows kernel-mode rootkit that can conceal malware…
A suspected Microsoft Power Pages configuration failure has been linked to the exposure of roughly 27 million records across 13 organizations, after the data-extortion group…
A newly identified Linux botnet dubbed Evooo1Bot is targeting vulnerable internet-facing routers, edge appliances, cameras, and enterprise systems, combining Mirai-derived DDoS capabilities with proxy relaying,…
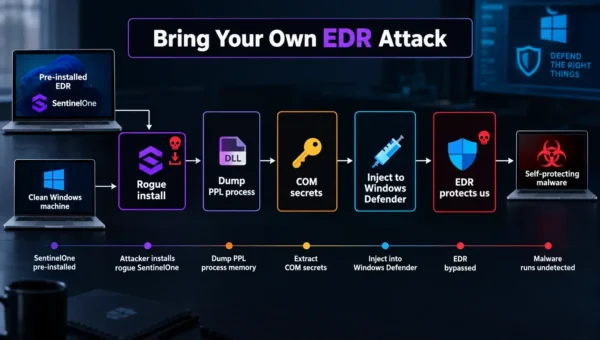
Security researchers have introduced a new technique called “Bring Your Own EDR” (BYOEDR) that exploits legitimate SentinelOne components to bypass Windows Protected Process Light (PPL)…
A growing underground market is turning mature malware-evasion techniques into subscription products. An analysis of 24 active crypting-service vendors shows that customers can now buy…
A newly disclosed Windows attack technique, dubbed “Download More RAM,” can undermine Virtualization-Based Security (VBS), bypass Hypervisor-Protected Code Integrity (HVCI), and disable endpoint protections including…
A newly disclosed universal deserialization gadget chain shows how a single unsafe Marshal.load operation can reportedly produce remote command execution in Ruby 4.0.6, underscoring the…