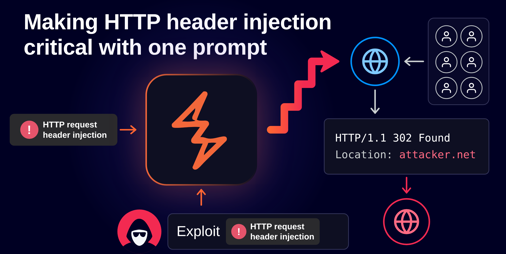
Making HTTP header injection critical with one prompt
Published: Wednesday, 4 November 2026 at 15:12 UTC Updated: Wednesday, 4 November 2026 at 15:12 UTC You can now escalate HTTP header injection to a…
Published: Wednesday, 4 November 2026 at 15:12 UTC Updated: Wednesday, 4 November 2026 at 15:12 UTC You can now escalate HTTP header injection to a…
Published: Tuesday, 27 October 2026 at 14:29 UTC Updated: Tuesday, 27 October 2026 at 14:29 UTC I tested eight popular SVG sanitizers and bypassed six…
Published: Tuesday, 6 October 2026 at 17:14 UTC Updated: Tuesday, 6 October 2026 at 17:14 UTC Have you ever felt like a model isn’t actually…
Published: Monday, 5 October 2026 at 15:04 UTC Updated: Monday, 5 October 2026 at 15:11 UTC I’m delighted to introduce Alex, my fellow swigger who…
Published: Wednesday, 23 September 2026 at 14:00 UTC Updated: Wednesday, 23 September 2026 at 14:00 UTC How many bugs have you missed because you didn’t…
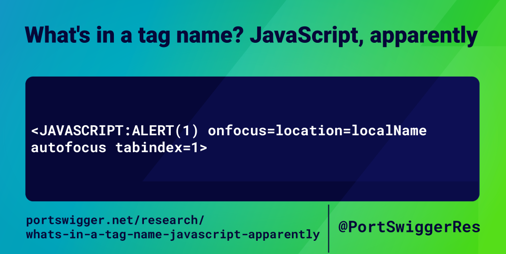
I was on my laptop, as I often am when there’s rubbish on telly, and found myself wondering what characters are allowed in a tag.…
In this post, I’ll share my approach to developing custom automation to aid research into under-appreciated attack classes and (hopefully) push the boundaries of web…
The single-packet attack is a new technique for triggering web race conditions. It works by completing multiple HTTP/2 requests with a single TCP packet, which…
This is a gif of the exfiltration process (We’ve increased the speed so you’re not waiting around for 1 minute). Read on to discover how…
Security research involves a lot of failure. It’s a perpetual balancing act between taking small steps with a predictable but boring outcome, and trying out…
Update: The results are in! Check out the final top ten here or scroll down to view all nominations Over the last year, numerous security…
In this post we’ll show you how Java handles unicode escapes in source code strings in a way you might find surprising – and how…