Stealing HttpOnly cookies with the cookie sandwich technique
In this post, I will introduce the “cookie sandwich” technique which lets you bypass the HttpOnly flag on certain servers. This research follows on from…
In this post, I will introduce the “cookie sandwich” technique which lets you bypass the HttpOnly flag on certain servers. This research follows on from…
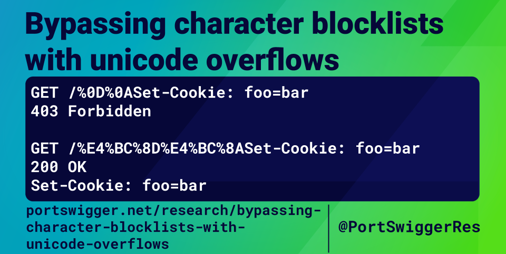
Unicode codepoint truncation – also called a Unicode overflow attack – happens when a server tries to store a Unicode character in a single byte.…
Welcome to the Top 10 Web Hacking Techniques of 2024, the 18th edition of our annual community-powered effort to identify the most innovative must-read web…
Have you ever wondered how many vulnerabilities you’ve missed by a hair’s breadth, due to a single flawed choice? We’ve just released Shadow Repeater, which…
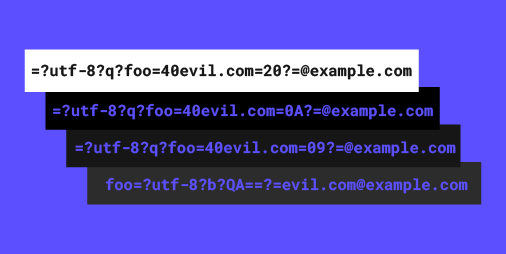
Introduction In this post, we’ll show precisely how to chain round-trip attacks and namespace confusion to achieve unauthenticated admin access on GitLab Enterprise by exploiting…
Tired of repeating yourself? Automate your web security audit trail. In this post I’ll introduce a new Burp AI extension that takes the boring bits…
Control characters like SOH, STX, EOT and ETX were never meant to run your code – but in the world of modern terminal emulators, they…
Manual testing doesn’t have to be repetitive. In this post, we’re introducing Repeater Strike – a new AI-powered Burp Suite extension designed to automate the…
Sometimes people think they’ve found HTTP request smuggling, when they’re actually just observing HTTP keep-alive or pipelining. This is usually a false positive, but sometimes…
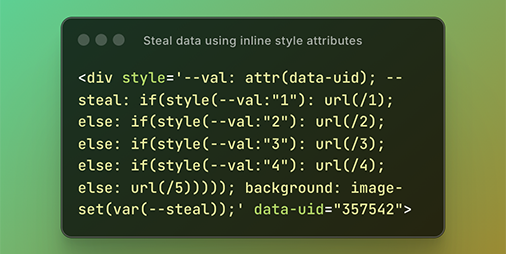
I discovered how to use CSS to steal attribute data without selectors and stylesheet imports! This means you can now exploit CSS injection via style…
Browsers added cookie prefixes to protect your sessions and stop attackers from setting harmful cookies. In this post, you’ll see how to bypass cookie defenses…
Many testers and tools give up the moment a protocol upgrade to WebSocket occurs, or only perform shallow analysis. This is a huge blind spot,…