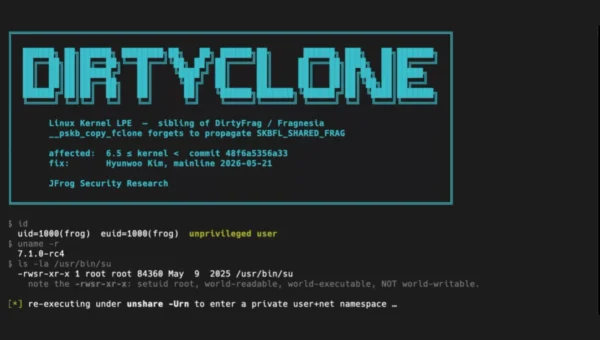
Critical Linux Kernel Flaw Allows Unprivileged Users to Gain Full Root Access
A newly disclosed flaw in the Linux kernel’s traffic-control subsystem, now assigned CVE-2026-46331 and referred to as “Pedit COW,” has been found to grant any…
A newly disclosed flaw in the Linux kernel’s traffic-control subsystem, now assigned CVE-2026-46331 and referred to as “Pedit COW,” has been found to grant any…
Anthropic has officially restored access to its Claude Mythos 5 artificial intelligence model for a select group of U.S. organizations tasked with defending critical national…
A critical Local Privilege Escalation flaw has been uncovered within the Linux kernel, allowing unprivileged local users to seamlessly gain root access by manipulating the…
Hackers have weaponized a WinRAR path-traversal flaw tracked as CVE-2025-8088 to silently plant a Startup shortcut and run a multi-stage PowerShell loader that maps a…
A critical server-side template injection (SSTI) vulnerability in FOSSBilling, tracked as CVE-2026-28496, is exposing instances to potential full database compromise and remote code execution (RCE),…
Japan’s defense infrastructure has faced scrutiny following an investigation that revealed members of the Japan Self-Defense Forces (JSDF) used counterfeit USB drives embedded with malware…
Water and wastewater systems have become strategic gray‑zone targets for Russia, China, and Iran, driven by chronic underinvestment and weak operational‑technology (OT) defenses that make…
Scammers are increasingly exploiting Shopify’s ecosystem and its Shop order-tracking app to deliver fraudulent invoices directly into users’ purchase histories, marking a shift from traditional…
A fresh supply-chain wave by the Shai-Hulud/Hades family that infected 20 npm packages in the Leo/RStreams ecosystem, an AWS-native event streaming SDK widely used for…
Google has announced a significant enhancement to its AI platform with the release of Gemini 3.5 Flash, which now includes native support for agentic computer…
LokiBot, a long-lived infostealer first advertised in May 2015, continues to evolve. Recent samples demonstrate deliberate attempts to evade static detection and frustrate analysis by…
ManageEngine has disclosed a critical account takeover vulnerability, tracked as CVE-2026-11374, affecting various integrated products within its AD360 identity and access management suite. The flaw…