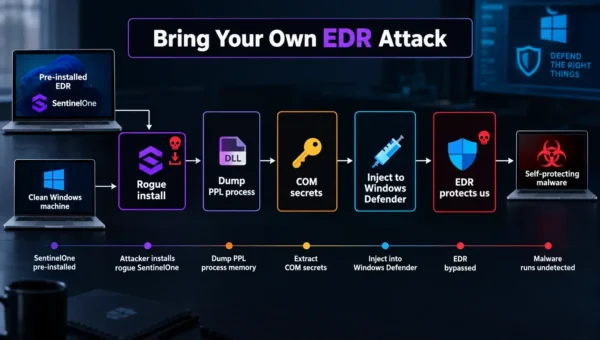
New Bring Your Own EDR Attack Turns SentinelOne Into Trojan Horse to Bypass Windows PPL
Security researchers have introduced a new technique called “Bring Your Own EDR” (BYOEDR) that exploits legitimate SentinelOne components to bypass Windows Protected Process Light (PPL)…