Trump Targets Foreign Technology in New U.S. Power Grid Security Order
Trump Targets Foreign Technology in New U.S. Power Grid Security Order Pierluigi Paganini August 28, 2026 Trump targets foreign-made power grid equipment, citing cyber, sabotage…
Trump Targets Foreign Technology in New U.S. Power Grid Security Order Pierluigi Paganini August 28, 2026 Trump targets foreign-made power grid equipment, citing cyber, sabotage…
On the windswept plains just south of Tibet’s second-largest city, the towering smart inspection systems and automated cargo gantries of a brand-new international land port…
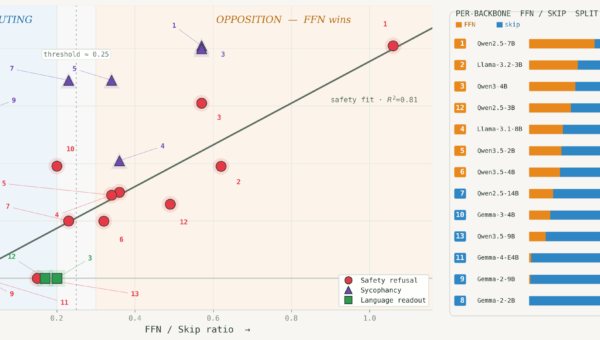
Introducing a New Angle on LLM Safety Our previous research on logit-gap steering demonstrated that the safety guardrails of an aligned LLM can be bypassed…
Overall, Seker noted, AI changes the economics of vulnerability exploitation more than it changes the underlying vulnerability. Attackers are using AI to analyze disclosures, generate…
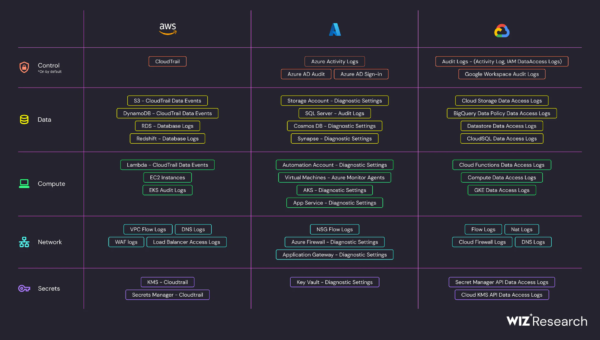
Cloud logging is a critical piece of any cloud detection and response program. Logs have always been an important source of information for the security…
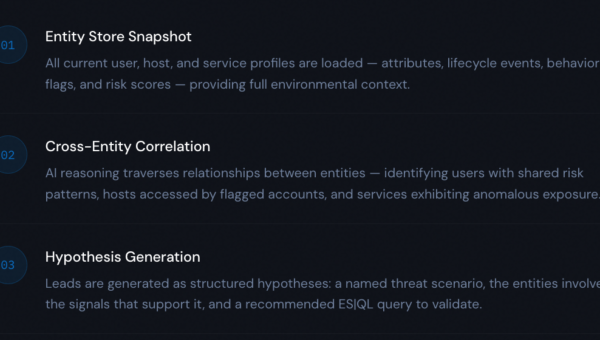
Threat hunting has always been a human art; a practitioner staring at logs, forming a hypothesis, and patiently chasing it down. What if the hardest…
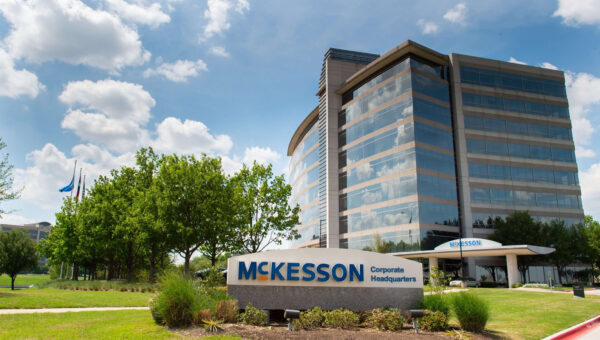
Healthcare and pharmaceutical distribution giant McKesson has disclosed a cybersecurity incident involving unauthorized access to third-party applications and data theft, with the ShinyHunters extortion group…
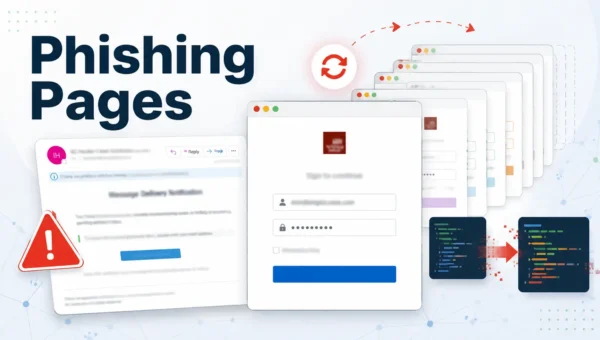
Hackers are making some phishing pages harder to track by changing the code delivered to every visitor. An examined operation served a credential-stealing form whose…
There’s no question that AI has transformed healthcare research and completely changed the trajectory of the healthcare industry. What would have taken researchers months to uncover even…
Attackers are actively exploiting a critical, unauthenticated remote code execution (RCE) vulnerability in PaperCut NG and PaperCut MF, widely used print management software, security researchers…
A newly analyzed phishing operation is using server-side polymorphism to generate a distinct credential-harvesting page for virtually every request, undermining detection approaches built around file…
In this interview with Help Net Security, Prasad Tharippala, Field CISO at Versa, explains what organizations miss when they run open-weight models in house. He…