Meet the Huntress MCP Server
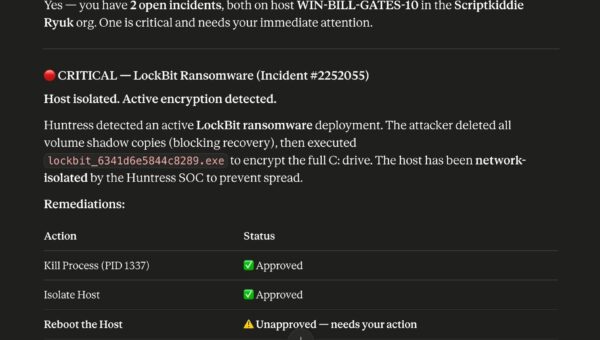
Security data is only useful if you can get to it when you need it. For most partners and customers, that means logging into the…
Security data is only useful if you can get to it when you need it. For most partners and customers, that means logging into the…
Microsoft has patched a maximum-severity vulnerability in the Entra ID identity and access management (IAM) platform that has been exploited in attacks. Formerly known as…
Suspected Russian cyber-espionage groups are increasingly turning ordinary sign-in and device-linking features into tools for account takeover. Their latest campaigns do not depend on breaking…
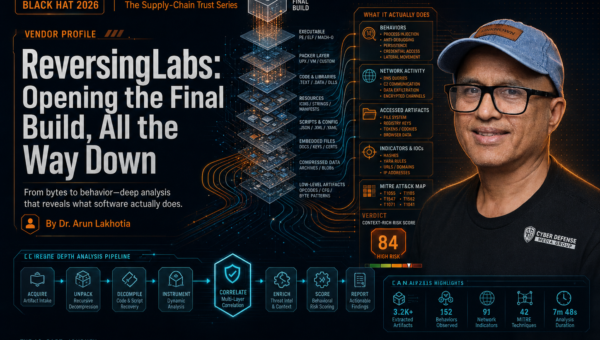
Black Hat 2026 Vendor Profile — Cyber Defense Magazine By Dr. Arun Lakhotia Black Hat 2026: The Supply-Chain Trust Series — Cyber Defense Magazine. Part…
A business email compromise campaign is using emoji-filled JScript to conceal an Agent Tesla v4 infostealer designed to steal browser, email, and messaging credentials. The…
Citrix has patched two vulnerabilities in NetScaler ADC and NetScaler Gateway, including a critical authentication bypass flaw tracked as CVE-2026-19490, and is urging customers to…
Researcher Jeremiah Fowler found a cloud database containing more than 9 million image files accessible without authentication, WIRED reports. The leaky bucket, containing some 450…
Ravie LakshmananAug 21, 2026Vulnerability / Enterprise Security A newly disclosed security flaw in GitLab has come under active exploitation within days of public disclosure, according…
It’s a subject that attracts endless debate: will AI replace whole swathes of human jobs and create an exodus from white collar professions? The trigger…
Key points A Senate estimates question from Senator Jane Hume has produced the first real census of AI subscriptions across federal government, with 67 entities…
North Korean hackers are responsible for a new open source software (OSS) supply chain attack targeting the Rust ecosystem, cybersecurity firm Wiz reports. The attack…
Poland’s CERT Warns of Active Exploitation of Critical Zimbra Collaboration Suite Flaw Pierluigi Paganini August 21, 2026 CERT Polska confirmed active exploitation of CVE-2026-73570, a…