Airservices Australia wants to build an ‘AI front door’
Key points Airservices Australia is exploring a “broker platform” within its AWS tenancy to act as a single governed entry point for all AI interactions.…
Key points Airservices Australia is exploring a “broker platform” within its AWS tenancy to act as a single governed entry point for all AI interactions.…
Rockwell Automation on Tuesday informed customers that patches or workarounds are available for more than a dozen vulnerabilities discovered across its industrial automation products. Only…
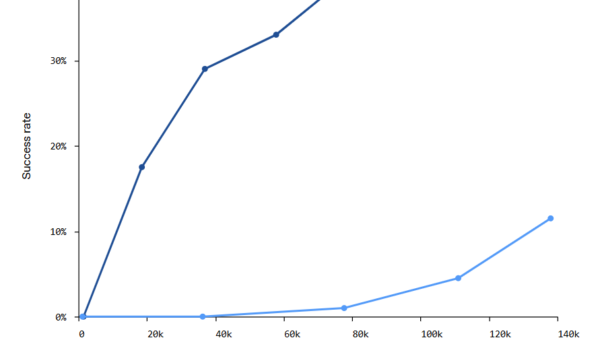
OpenAI Astra Brings Autonomous Zero-Day Exploitation to AI Pierluigi Paganini September 02, 2026 OpenAI says Astra can autonomously find zero-days and build exploits, marking its…
The FBI said a 17-year-old from Maine is the first child federally charged and adjudicated for crimes stemming from their involvement in 764, a violent…
Yubico has expanded its partnership with OpenAI into Australia and nine other countries as OpenAI begins requiring hardware-backed passkeys for members of its Trusted Access…
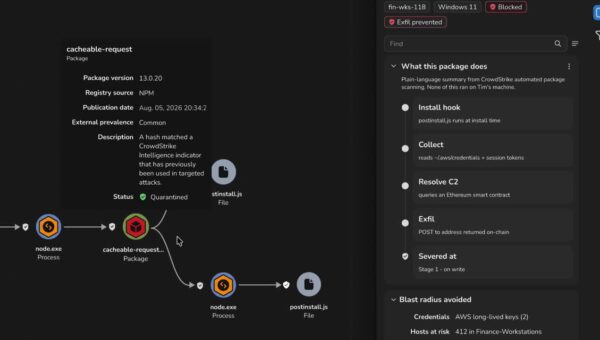
Software supply chain attacks pose a critical enterprise threat. In the first half of 2026, these attacks increasingly used malicious software packages uploaded to public…
Repeats a June attack chain What makes this issue especially significant is the timing and the pattern, he pointed out. “This is essentially a rerun…
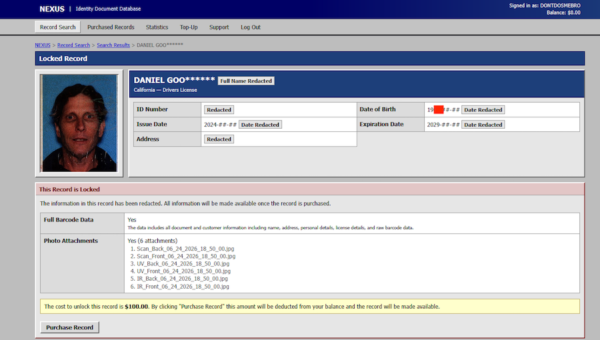
The timing of newly available scans—typically within a day, if not hours, of me and a small sample of other victims presenting them at rental…
Wiz has been authorized by the Common Vulnerability and Exposures (CVE®) Program as a CVE Numbering Authority (CNA). This milestone is thrilling and humbling. Not…
In our latest webinar, Flashpoint Vice President of Intelligence, Ian Gray, briefed security leaders on the evolving threat environment, providing critical insights from the Flashpoint…
We are thrilled to announce today that Elastic has entered into an agreement to acquire Keep Alerting Ltd (“Keep”), an open source AIOps company. The…
Attackers are actively exploiting CVE-2026-9586, an unauthenticated SQL injection vulnerability in the Sangoma Switchvox VoIP platform that can lead to remote code execution. According to…