ENISA: Frontier AI Is Changing the Speed of Cyberattacks. Europe Needs to Catch Up
ENISA: Frontier AI Is Changing the Speed of Cyberattacks. Europe Needs to Catch Up Pierluigi Paganini September 14, 2026 Frontier AI is compressing the attack…
ENISA: Frontier AI Is Changing the Speed of Cyberattacks. Europe Needs to Catch Up Pierluigi Paganini September 14, 2026 Frontier AI is compressing the attack…
The vulnerability could let unauthenticated users access sensitive files from software-development environments. Source link
Five alleged leaders of the South African wing of Black Axe, a global cybercrime group with operations spanning dozens of countries, were extradited to the…
The number of suspicious credit card transactions involving pre-orders for the latest iPhone models has surged to more than 1,200 in Hong Kong, involving HK$25…
We ‘re excited to announce the release of “The Financial Services Cloud Security Playbook,” a practical guide that aims to aid in transforming and scaling…
An alert may be the first sign a security team sees, but it rarely marks the beginning of an attack. Before an intrusion reaches the…
In the first article in this multipart series, malware researchers on the Elastic Security Labs team give a short introduction about the REMCOS threat and…
Microsoft has released emergency out-of-band Windows updates to fix Remote Desktop Services failures caused by this month’s security updates, along with Hyper-V and USB audio…
Researchers have uncovered an exposed attacker-controlled staging server containing evidence of a wide-ranging intrusion targeting 3BB, the consumer brand operated by Thailand’s Triple T Broadband.…
For the best part of a decade, abusive deepfake “pornography” websites have published thousands of nonconsensual videos depicting women, including high-profile celebrities, politicians, and public…
When the SOC Stops Following Playbooks and Starts Thinking: Automating the SOC with AI Agents Skip to content We use cookies to ensure that we…
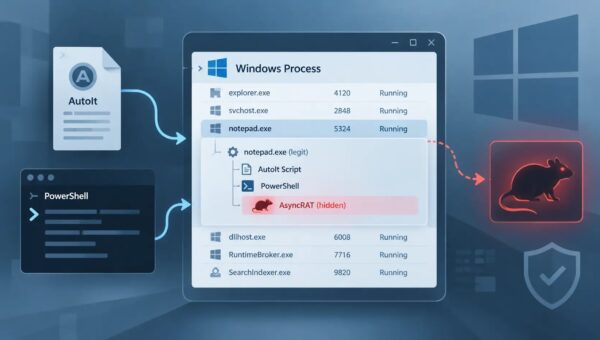
A five-stage AsyncRAT campaign that chains a socially engineered batch file, hidden PowerShell execution, AutoIt abuse and process injection to conceal a .NET remote-access trojan…