Many organizations use bug bounty programs to help them protect their ever-expanding attack surface and achieve attack resistance. Bug bounties, with ethical hackers at the helm, uncover critical and severe vulnerabilities before bad actors and deliver better protection against cyberattacks. But what is a bug bounty, and should your organization have one?

Related Articles
All Mix →AI Novels Are Coming | Daniel Miessler
It’s about to get a lot easier to write a decent novel. I’d guess that within 1-3 years, being an “author” of a novel is…
AI’s Total Addressable Market
 The total market size (TAM) for AI is a combination of two (2) primary components: 1. The total cost of human workforces 2.…
LIGHTS? 60 seconds on why i think a dynamic light setup is important.
LIGHTS? 60 seconds on why i think a dynamic light setup is important. Source link
Free Will vs. Determinism as the Core of Political Disagreement
Table of Contents No Longer Academic Evidence Conclusion Ultimately, there are two primary political belief systems, and they are poorly captured by any label such…
[tl;dr sec] #170 – Prototype Pollution, Fuzzing, SOC Metrics
Table of Contents Focusing on the Right Stuff 📢 Drata’s Compliance Trends Report 2023 📜 In this newsletter… Web Security 📢 We Hack Purple –…
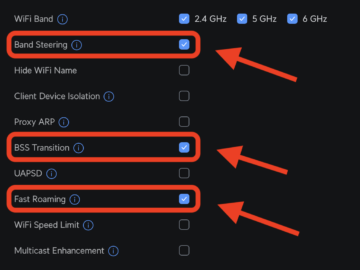
Fixing Ubiquiti WiFi Roaming
The three settings I had to enable to get proper WiFi roaming The problem I’m a massive fan of Ubiquiti stuff, but even after upgrading…