Leading AI companies have learned important lessons from recent incidents, the official said, and regulation isn’t necessary to preserve those lessons.
Leading AI companies have learned important lessons from recent incidents, the official said, and regulation isn’t necessary to preserve those lessons.
The tech giant’s announcement underscores the insufficiency of companies’ existing software supply-chain security practices. Source link
Deloitte-NASCIO study shows AI, budget pressures are forcing states to make tough decisions. Source link
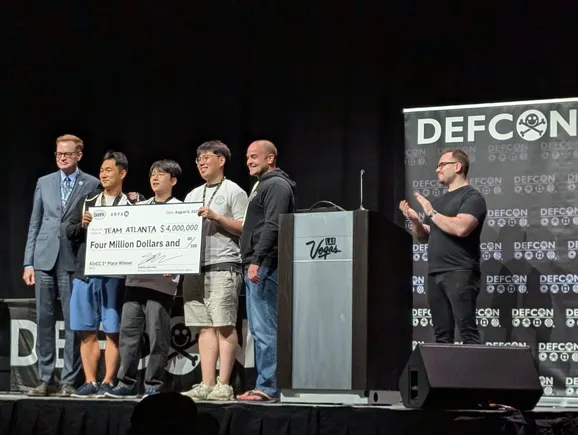
Listen to the article 5 min This audio is auto-generated. Please let us know if you have feedback. LAS VEGAS — The Defense Advanced Research Projects…
A hacking campaign targeting Oracle E-Business Suite customers may have begun as early as July, when hackers began chaining together vulnerabilities in the software, according…
Finding the time to train employees remains the biggest impediment to programs’ success, according to a new report. Source link
A zero-day vulnerability in a Microsoft-signed driver from Paragon Software is being exploited in ransomware attacks. CERT Coordination Center on Friday warned in a security…