UNC6783 Hackers Use Fake Okta Pages in Corporate Breach Campaign
Cybersecurity experts at Google Threat Intelligence Group (GTIG) have issued a warning about a new group of hackers, known as UNC6783, who are trying to…
Cybersecurity experts at Google Threat Intelligence Group (GTIG) have issued a warning about a new group of hackers, known as UNC6783, who are trying to…
Cybercrime operates like a legitimate, profit-driven economy, writes Subhalakshmi Ganapathy, chief IT security evangelist at ManageEngine, in a BusinessWorld article. Organized groups mirror corporate structures and…
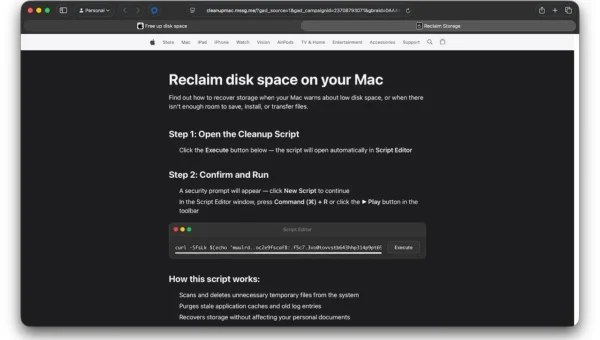
Security researchers at Jamf have uncovered a new ClickFix-style attack targeting Mac users via a fake Apple-themed webpage offering instructions on how to “reclaim disk…
Ravie LakshmananApr 10, 2026Malware / Blockchain Cybersecurity researchers have flagged yet another evolution of the ongoing GlassWorm campaign, which employs a new Zig dropper that’s designed…
In January 2026, 45 UK MPs submitted an Early Day Motion entitled “UK digital sovereignty strategy”. The motion pointed to the dependency of government services,…
When Microsoft reintroduced its redesigned Recall feature, security took center stage. The architecture was built around hardened components, including Virtualization-Based Security (VBS) enclaves, AES-256-GCM encryption,…
In this week’s weekly roundup, The Cyber Express summarizes key cybersecurity news across state-sponsored attacks, crypto ecosystem breaches, regulatory gaps, and mobile data exposure risks. …
The US National Highway Traffic Safety Administration has closed a probe into nearly 2.6 million Tesla vehicles over a feature allowing users to move cars…
Juniper Networks this week released patches for nearly three dozen vulnerabilities, including Junos OS and Junos OS Evolved bugs that could lead to privilege escalation,…
UAT-10362 linked to LucidRook attacks targeting Taiwan-based institutions Pierluigi Paganini April 10, 2026 LucidRook is Lua malware used in phishing attacks on NGOs and universities…
The flaw is tracked as CVE-2026-34197 and carries a high severity rating (CVSS 8.8). It affects ActiveMQ Classic versions prior to 5.19.4 and several 6.x…
New research from Comparitech underscores how exposed ICS (industrial control systems) continue to present a tangible risk to critical infrastructure, with 179 internet-facing ICS devices…