“CanisterWorm” supply chain malware attacks npm
A threat actor who stole credentials from a legitimate node package manager (npm) publisher has spread a persistent, worm-like malware across dozens of packages, security…
A threat actor who stole credentials from a legitimate node package manager (npm) publisher has spread a persistent, worm-like malware across dozens of packages, security…
Iran-linked actors use Telegram as C2 in malware attacks on dissidents Pierluigi Paganini March 23, 2026 Iran-linked actors use Telegram as C2 to spread malware…
When an admin from the organization activated the new hire’s EntraID account, the team observed that the new hire used an EntraID login from a…
The Cyber Readiness Institute (CRI), in partnership with the Center on Cyber and Technology Innovation (CCTI) at the Foundation for Defense of Democracies and with…
The Office of the Director of National Intelligence’s Annual Threat Assessment 2026 makes clear that cyberspace is now a primary arena of conflict, with state…
Before you pop the bubbly and count down to a new year, let’s reminisce for a moment. Looking back on the past 365 days, it…
The U.S. Federal Bureau of Investigation (FBI) warned network defenders that Iranian hackers linked to the country’s Ministry of Intelligence and Security (MOIS) are using…
A new wave of supply chain attacks is hitting the npm ecosystem through a self-propagating malware campaign known as CanisterWorm. The threat, linked to a…
QNAP has released an urgent security advisory regarding a critical vulnerability affecting its QVR Pro application, a widely deployed network video surveillance solution. Disclosed on…
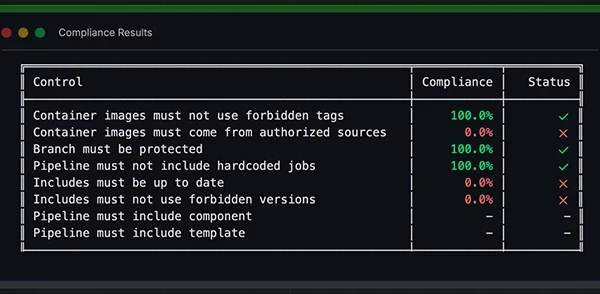
GitLab CI/CD pipelines often accumulate configuration decisions that drift from security baselines over time. Container images get pinned to mutable tags, branches lose protection settings,…
Last week on Malwarebytes Labs: Stay safe! We don’t just report on threats—we help safeguard your entire digital identity Cybersecurity risks should never spread beyond…
Ravie LakshmananMar 23, 2026Vulnerability / Endpoint Security Threat actors are suspected to be exploiting a maximum-severity security flaw impacting Quest KACE Systems Management Appliance (SMA),…