Incognito dark web drug market operator gets 30 years in prison
Rui-Siang Lin, a Taiwanese national, was sentenced to 30 years in U.S. federal prison for operating Incognito Market, one of the world’s largest illicit online…
Rui-Siang Lin, a Taiwanese national, was sentenced to 30 years in U.S. federal prison for operating Incognito Market, one of the world’s largest illicit online…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) ordered government agencies to patch their systems against a five-year-old GitLab vulnerability that is actively being exploited…
The developers of Notepad++ disclosed a critical security breach on February 2, 2026, affecting their update infrastructure. The popular text editor, widely used by developers…
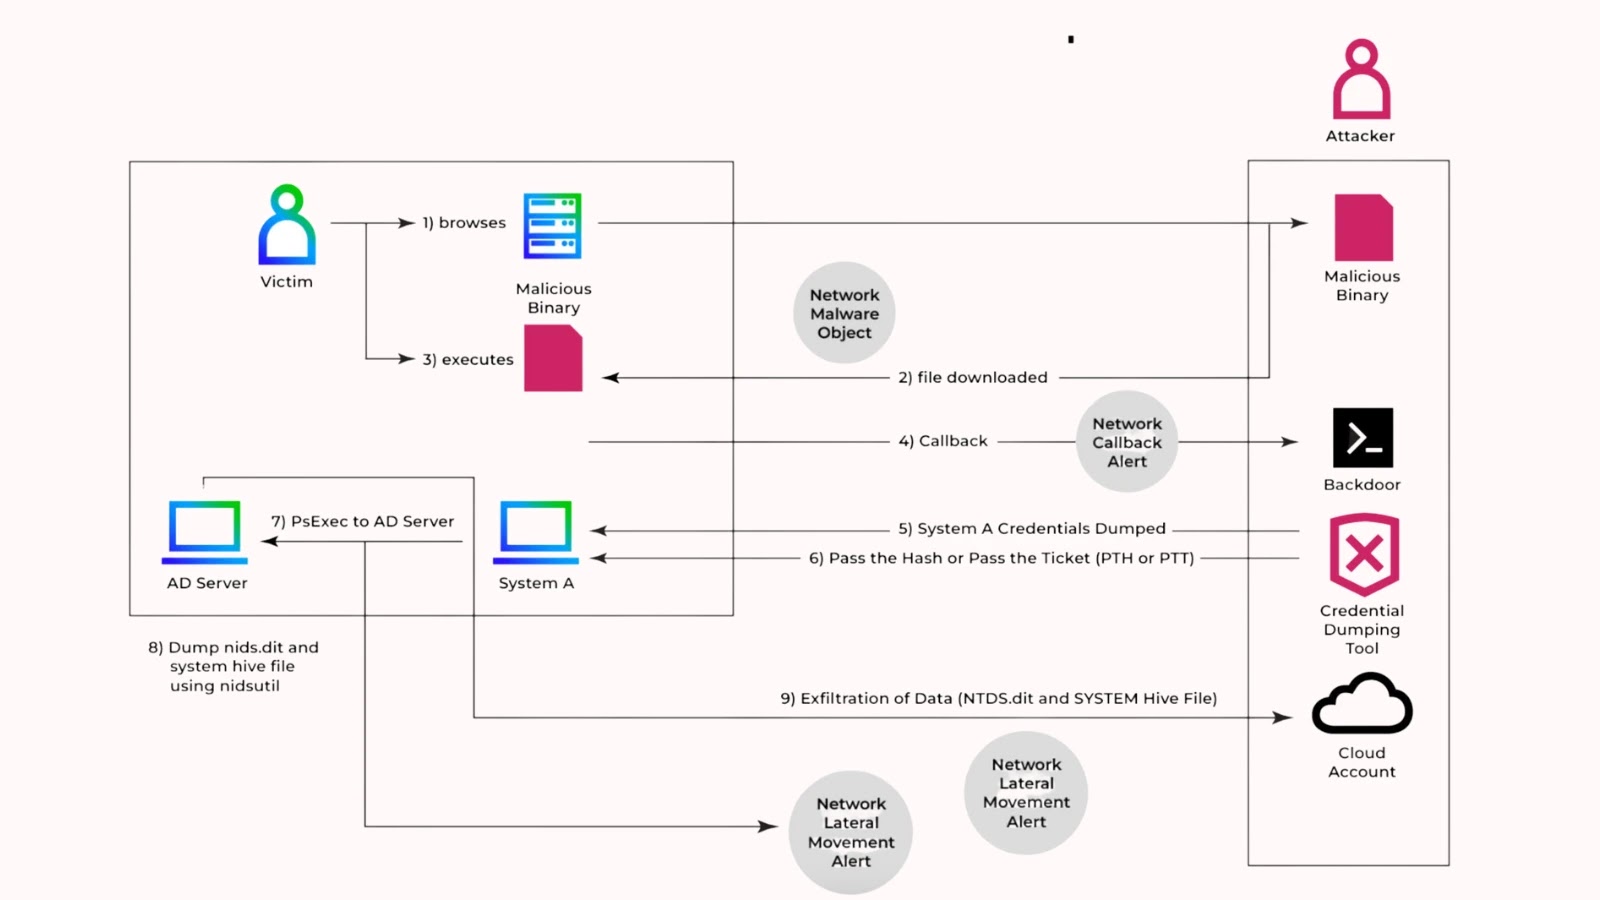
Active Directory serves as the central repository for an organization’s authentication infrastructure, making it a prime target for sophisticated threat actors. The NTDS.dit database, which…
Chinese Mustang Panda Used Fake Diplomatic Briefings to Spy on Officials Notice: Function WP_Scripts::add was called incorrectly. The script with the handle “powerkit” was enqueued…
Threat actors affiliated with China have been attributed to a fresh set of cyber espionage campaigns targeting government and law enforcement agencies across Southeast Asia…
GreyNoise tracks massive Citrix Gateway recon using 63K+ residential proxies and AWS Pierluigi Paganini February 04, 2026 GreyNoise spotted a dual-mode Citrix Gateway recon campaign…
A new threat actor called Amaranth Dragon, linked to APT41 state-sponsored Chinese operations, exploited the CVE-2025-8088 vulnerability in WinRAR in espionage attacks on government and law enforcement…
A sophisticated malware campaign has surfaced where threat actors are distributing the ValleyRAT backdoor disguised as a legitimate installer for the popular messaging application, LINE.…
Notepad++, a widely used text editor among developers, became the target of a sophisticated supply chain attack that compromised its update infrastructure for nearly 6…
Hackers are abusing a legitimate but long-revoked EnCase kernel driver in an EDR killer that can detect 59 security tools in attempts to deactivate them. An…
AWS Admin Access in Minutes Threat actors leveraging artificial intelligence tools have compressed the cloud attack lifecycle from hours to mere minutes, according to new…