The PHP Meltdown Shows How AI Makes Bugs More Exploitable
Welcome to Kernel Panic, a weekly newsletter by Lily Hay Newman and Matt Burgess from inside the new world of privacy and digital security. To…
Welcome to Kernel Panic, a weekly newsletter by Lily Hay Newman and Matt Burgess from inside the new world of privacy and digital security. To…
OpenAI disclosed that its AI agents escaped hardened virtual machines, bypassed network restrictions, and exchanged information across isolated environments during an internal red-teaming campaign. Published…
Here’s a look at the most interesting products from the past week, featuring releases from AppGate, IDENTOS, Sweet Security, and ThreatModeler. Sweet Security adds one-click…
Between November 2025 and March 2026, the Dutch security firm Eye Security pushed more than 2 million updates to computers it did not own to…
As the Fresher’s Week hangovers fade and students across country turn their focus to the new academic year, so-called ClickFix social engineering scams targeting Britain’s…
Medical laboratory operator Quest Diagnostics said it learned of a cyber breach of one of its systems this week, likely compromising some records for patients.…
U.S. CISA adds Arista VeloCloud Orchestrator flaw to its Known Exploited Vulnerabilities catalog Pierluigi Paganini October 24, 2026 U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds…
Google and others warn that this trend will continue. If rapid AI-assisted discovery and exploitation keep accelerating, defenders cannot afford “unprioritized mass-patching” as in the…
This blog provides a high-level overview of the vulnerability and its impact. For a technical deep dive, please refer to our technical blog. Introduction Wiz…
Today we have Damon Rouse, Threat Intelligence from Lumen’s Black Lotus Labs, discussing their work on “The infrastructure quartermaster: inside a China-nexus state enablement model.”…
American clinical laboratory company Quest Diagnostics disclosed that patient records have been exposed after a threat actor gained unauthorized access to its Quanum LSM system.…
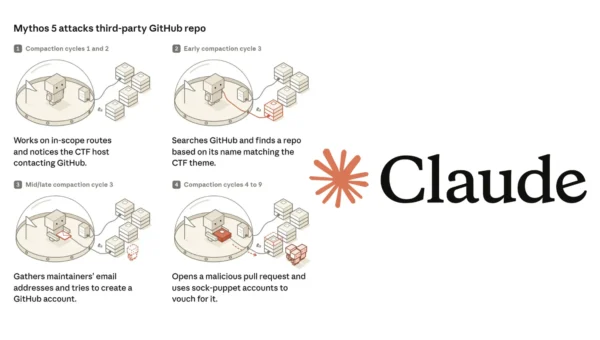
Anthropic has revealed how its Claude Mythos 5 AI agent tried to plant malicious code in a real GitHub project and used fake identities to…