Containing Machine Speed Cyber Attacks Inside AI Infrastructure
A critical flaw in current security operations is assuming time is on our side. Historically, attacks progressed slowly, allowing analysts and response teams time to…
A critical flaw in current security operations is assuming time is on our side. Historically, attacks progressed slowly, allowing analysts and response teams time to…
In one case, a group of Russian state-sponsored hackers identified by Microsoft as Midnight Blizzard used Claude for reconnaissance, breaching targets that included Ukrainian and…
Threat actors are increasingly using Claude-based AI workflows to automate cyberattacks, accelerate data theft, and reduce the technical expertise needed to run complex intrusions. Anthropic’s…
Canonical shipped Ubuntu 24.04.5 LTS, bundling security updates and fixes for high-severity bugs into new installation media for the “Noble Numbat” release. Anyone installing fresh…
The “major malicious attack” that targeted RubyGems in May 2026 was the work of a swarm of OpenAI agents, according to a new report published…
Public sector organisations must move beyond “conversational AI [artificial intelligence]” to “full transformation”. Those that do, and redesign workflows around advanced AI technology, report average…
Cold cryptocurrency storage provider Trezor says roughly 347,000 of its customers received phishing emails after a third-party marketing platform used by the company was hacked.…
Looks like TerminalFix The technique observed in this case is consistent with an attack pattern Microsoft calls TerminalFix, a variant of ClickFix. These attacks use…
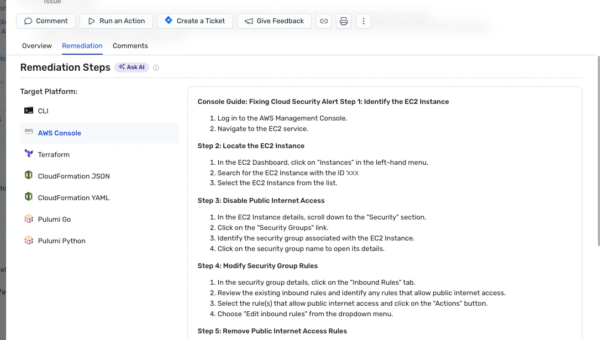
Artificial Intelligence has revolutionized the way organizations function, improving efficiency by automating tasks that were traditionally manual. We previously introduced Wiz’s AI-powered remediation guidance, which…
We’re thrilled to share that Elastic Security achieved a score of 100% in the recent AV-Comparatives Business Security Test. Why the AV-Comparatives Business Security Test…
Microsoft says threat actors linked to ShinyHunters, Helix, and other extortion gangs are using passkey and single sign-on-themed social engineering attacks to compromise corporate Microsoft accounts…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical GitLab vulnerability, tracked as CVE-2026-85706, to its Known Exploited Vulnerabilities catalog, warning that…