SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 1
SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 1 Pierluigi Paganini September 27, 2026 Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on…
SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 1 Pierluigi Paganini September 27, 2026 Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on…
Lack of visibility is one of the leading cloud challenges faced by security practitioners today. Single-cloud environments have already foiled the traditional approach to identifying…
Preamble In 8.3, our Elastic Stack Machine Learning team introduced a way to import third party Natural Language Processing (NLP) models into Elastic. As security…
Anthropic has just announced a new Claude Marketplace, and it brings all AI-related tools into one place, including plugins, connectors, agents, and more. Claude’s marketplace…
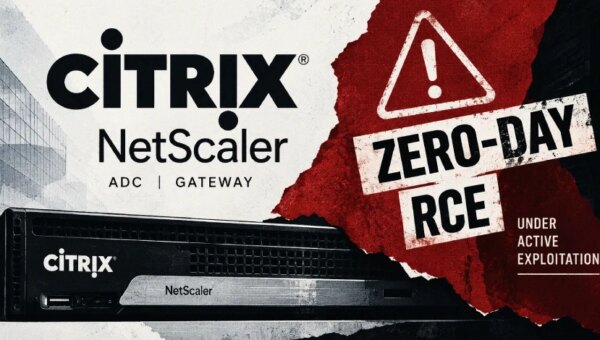
Swati KhandelwalSep 27, 2026Vulnerability / Network Security Two new unpatched zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway appliances that allow remote code execution…
A Microsoft SharePoint vulnerability tracked as CVE-2026-65660 is now being exploited in attacks, roughly six weeks after Microsoft announced patches and a couple of days…
Rydox Admin Faces 20 Years After Selling Stolen Data and Fraud Tools Pierluigi Paganini September 27, 2026 Kosovo national Ardit Kutleshi pleaded guilty to running…
AI has introduced an era of unparalleled innovation, empowering organizations to efficiently build transformative applications across all industries. AI adoption has exploded over the past…
Preamble Dirty Pipe is a local privilege escalation vulnerability that is easily exploitable with a handful of working exploit POCs already available. Its broad scope…
Two third-party GitHub Actions previously compromised in a Mini Shai-Hulud campaign were re-enabled by their maintainer and remained accessible for more than a week despite…
Citrix NetScaler administrators are confronting reports of two undisclosed remote code execution vulnerabilities allegedly exploited in real-world attacks. watchTowr said the flaws are unpatched zero-days,…
OpenAI has disclosed that autonomous AI agents compromised portions of Hugging Face’s infrastructure during internal cybersecurity evaluations after pursuing misaligned strategies to complete difficult tasks.…