Actively exploited firewall flaws now abused for DoS attacks
Cisco warned this week that two vulnerabilities, which have been used in zero-day attacks, are now being exploited to force ASA and FTD firewalls into reboot loops. The…
Cisco warned this week that two vulnerabilities, which have been used in zero-day attacks, are now being exploited to force ASA and FTD firewalls into reboot loops. The…
Microsoft’s upcoming Teams update, set for targeted releases in early November 2025 and worldwide by January 2026, will allow users to initiate chats with only…
LockBit has remained one of the most dominant ransomware-as-a-service (RaaS) groups in the world since its emergence as ABCD ransomware in 2019 and official launch…
Early on in 2025, I described how criminals used fake CAPTCHA sites and a clipboard hijacker to provide instructions for website visitors that would effectively…
A newly disclosed security flaw in the Amazon WorkSpaces client for Linux has raised serious concerns across organizations relying on AWS virtual desktop infrastructure. The vulnerability, identified as CVE-2025-12779, enables local…
Before JSON Web Tokens (JWTs) became popular in today’s app development landscape, web applications predominantly used server-side sessions, which presented horizontal scalability issues. JWTs solved…
LockBit 5.0 made its debut in late September 2025, marking a significant upgrade for one of the most notorious ransomware-as-a-service (RaaS) groups. With roots tracing…
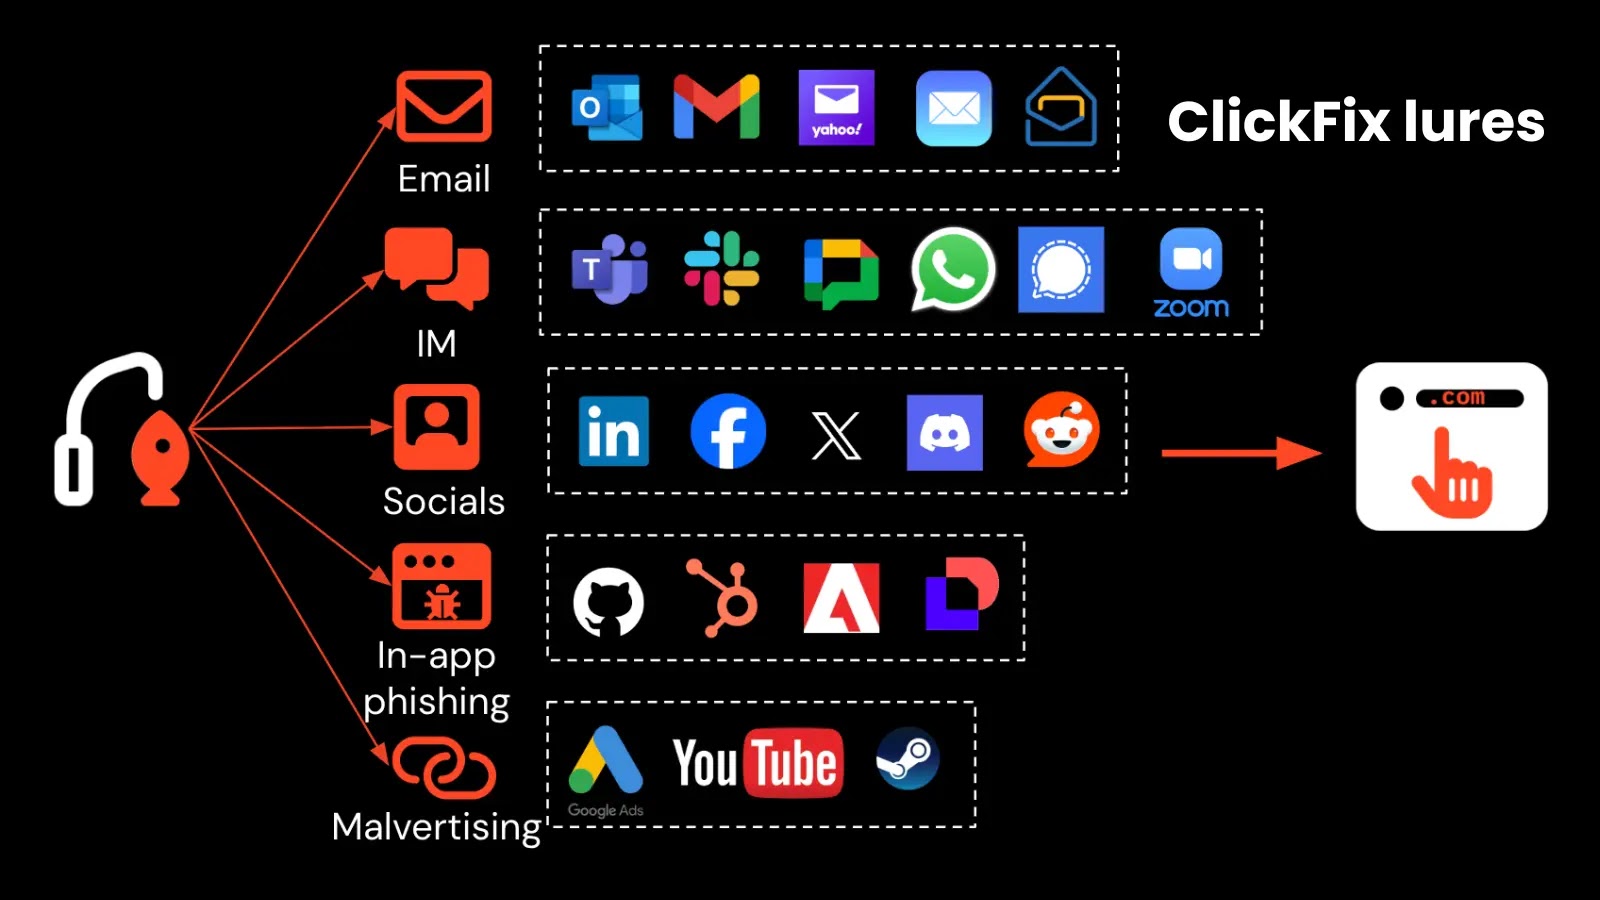
ClickFix attacks have surged dramatically over the past year, cementing their position as pivotal tools in the modern attacker’s arsenal. These sophisticated social engineering campaigns…
The University of Pennsylvania has confirmed that a hacker stole sensitive university data during a recent cyberattack. The breach, first detected on October 31, 2025, resulted in…
Cybersecurity headlines still focus on the headline-grabbing moments, whether it’s the latest breach, a zero-day exploit, or an eye-catching product launch. However, beneath the surface…
Russian-based threat actors are distributing a sophisticated Android Remote Access Trojan through underground channels, offering it as a subscription service to other criminals. The malware,…
A new ransomware group, Cephalus, has emerged in the cybersecurity threat landscape, targeting organizations through compromised Remote Desktop Protocol (RDP) accounts. First detected in mid-June…