OnlyFans, Discord ClickFix-Themed Pages Spread Epsilon Red Ransomware
A sophisticated new ransomware campaign is actively tricking internet users around the world by employing fake verification pages to spread a dangerous threat called Epsilon…
A sophisticated new ransomware campaign is actively tricking internet users around the world by employing fake verification pages to spread a dangerous threat called Epsilon…
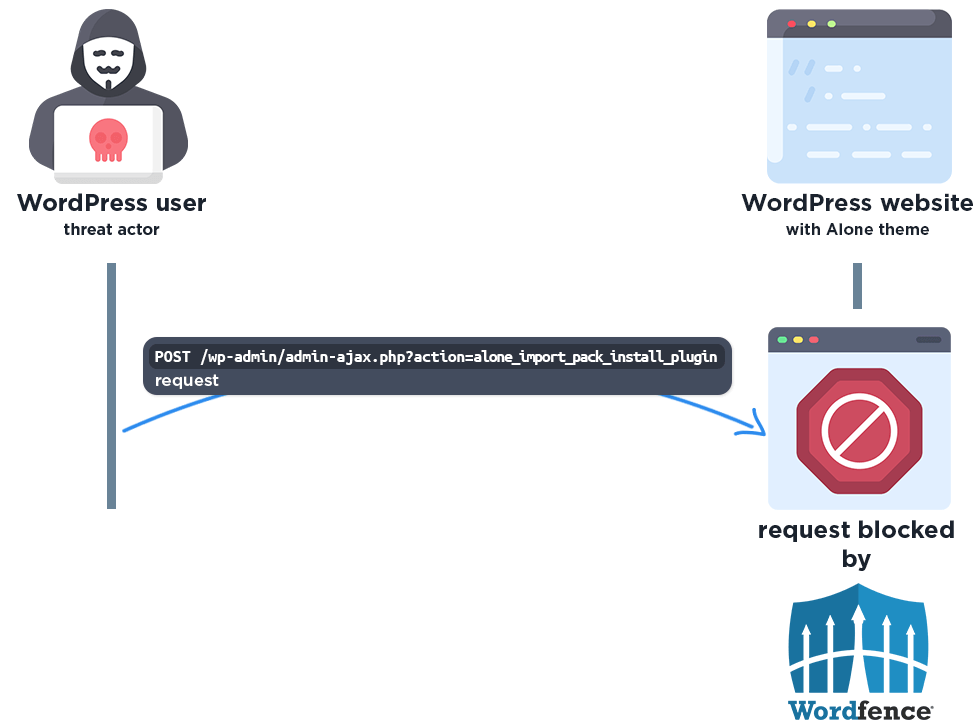
Attackers actively exploit critical zero-day in Alone WordPress Theme Pierluigi Paganini July 31, 2025 Hackers exploit a critical vulnerability, tracked as CVE-2025-5394 (CVSS score of…
A coalition of information-sharing groups urged their members on Wednesday to take additional steps to mitigate potential attacks by the cybercrime gang Scattered Spider, which…
A Russian nation-state threat group has been spying on foreign diplomats, managing continuous access to their communications and data in Moscow since at least 2024,…
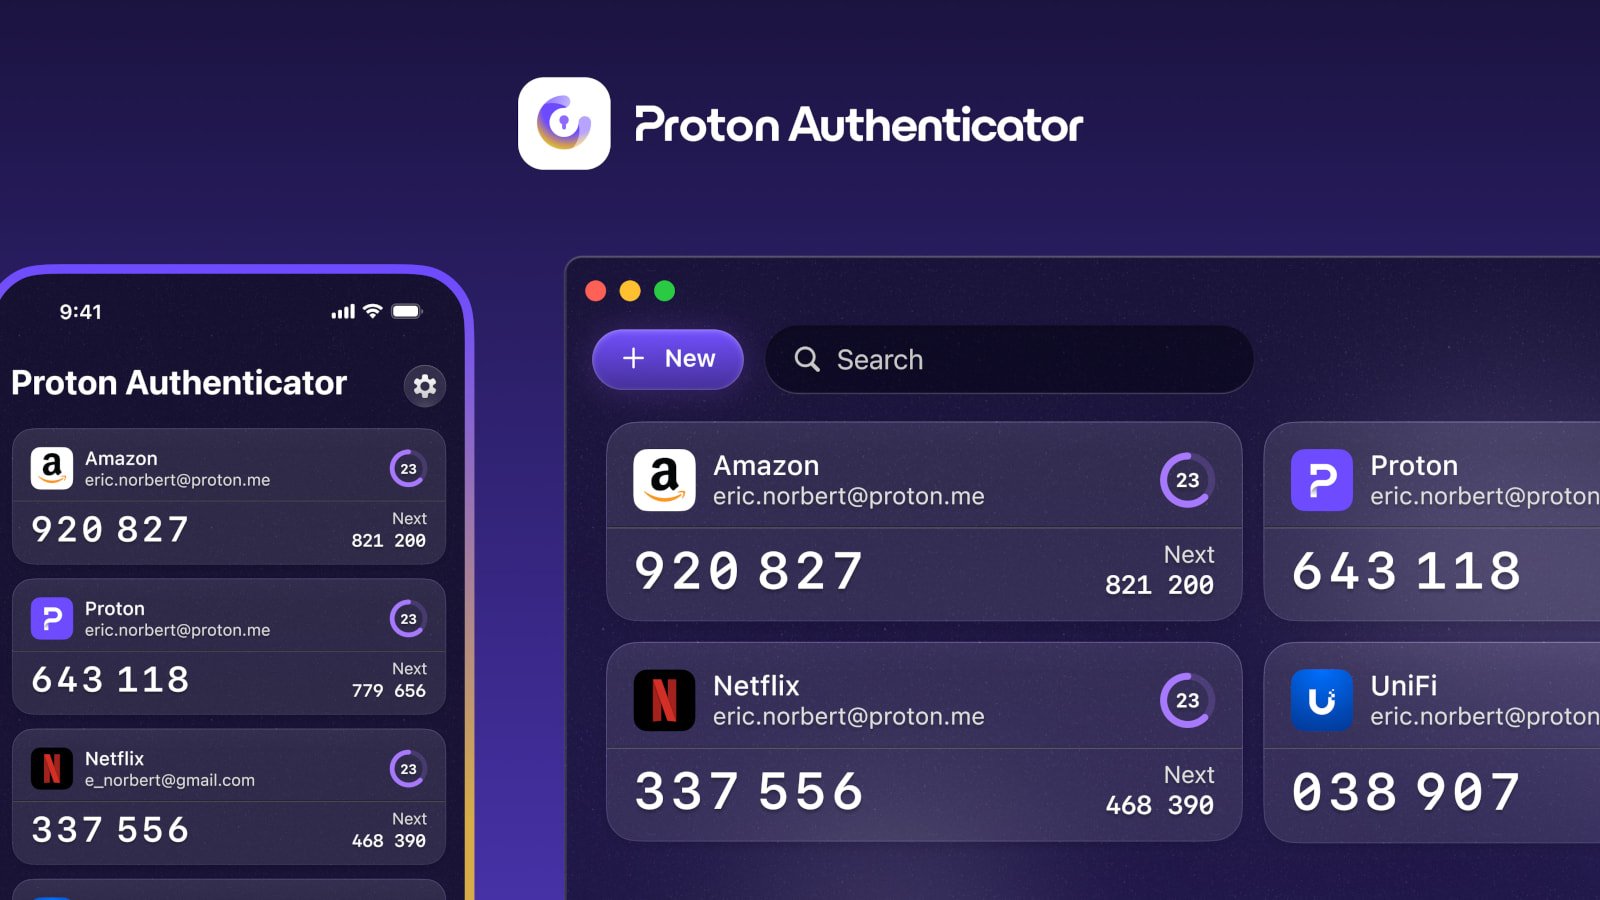
Proton has launched Proton Authenticator, a free standalone two-factor authentication (2FA) application for Windows, macOS, Linux, Android, and iOS. 2FA authenticator apps are offline tools that…
North Korean threat actors have evolved their cybercriminal operations into a sophisticated digital deception campaign that has successfully siphoned at least $88 million USD from…
The Russian state hacker group known as Turla has carried out some of the most innovative hacking feats in the history of cyberespionage, hiding their…
A Bangalore-based technology professional has been arrested in connection with a massive cryptocurrency theft worth approximately ₹379 crore ($44 million) from the popular Indian crypto…
The Competition and Markets Authority (CMA) has confirmed Microsoft and Amazon Web Services (AWS) will face “targeted and bespoke” interventions to curb behaviours the watchdog…
Listen to the article 3 min This audio is auto-generated. Please let us know if you have feedback. Dive Brief: Several major ransomware-as-a-service groups have…
Researchers have found that in roughly 80% of cases, spikes in malicious activity like network reconnaissance, targeted scanning, and brute-forcing attempts targeting edge networking devices…
Researchers at zLabs have been closely monitoring the DoubleTrouble banking trojan, a rapidly evolving malware strain that has shifted its tactics to exploit unsuspecting users…