Ledger Ethereum App Flaw: TestMachine Disclosure Dispute
Ledger CTO Charles Guillemet said on Aug. 23, 2026, that the company had fixed a clear-signing flaw in its Ethereum app two weeks before security…
Ledger CTO Charles Guillemet said on Aug. 23, 2026, that the company had fixed a clear-signing flaw in its Ethereum app two weeks before security…
New Zealand is moving ahead with a social media ban for under-16s, with the Government introducing the Online Safety (Minimum Age and Child Safety Risk…
Key points The ACSC is warning that CVE-2026-63077, a critical authentication bypass in JetBrains’ TeamCity On-Premises server, is under active local attack. Rated 9.8 out…
The cybersecurity agency CISA has instructed government organizations to immediately patch a critical vulnerability that has been widely exploited in attacks against Oracle WebLogic servers.…
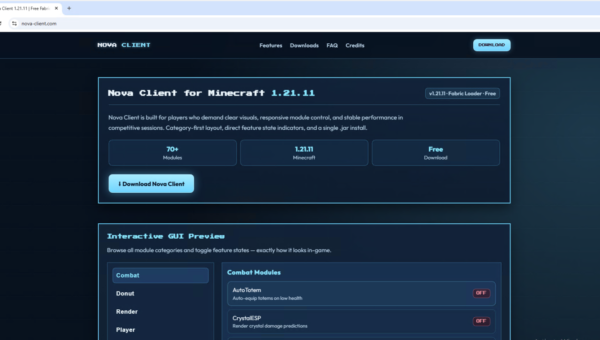
Fake Minecraft Sites Are Still Spreading WeedHack After C2 Takedown Pierluigi Paganini August 25, 2026 WeedHack Minecraft Malware Survives C2 Takedown: Fake Client Sites Still…
A new bipartisan Senate bill would require federal regulators to prepare the U.S. electric grid for cybersecurity threats from quantum computers and create a technical…
The Australian Cyber Security Centre (ACSC) has issued a high-severity alert warning that it has observed active exploitation of a vulnerability affecting TeamCity On-Premises servers…
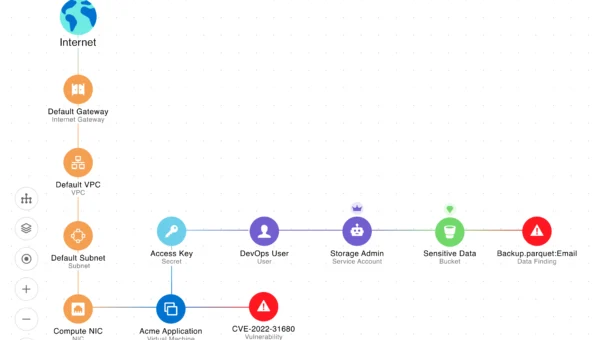
Responding fast to risks in your cloud environment is critical to ensure you can proactively remove issues before attackers discover them and they become active…
The U.S. Department of Justice announced a $400 million settlement with TikTok, ByteDance, and affiliated companies over allegations that they violated the Children’s Online Privacy…
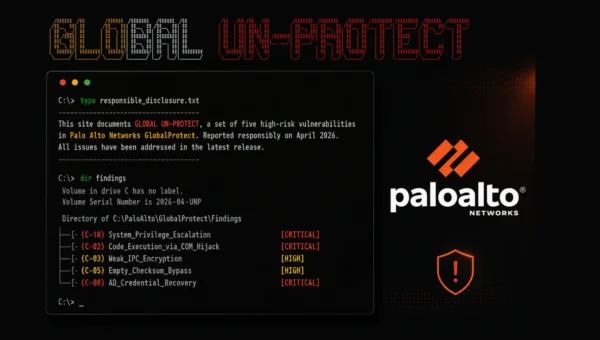
A security researcher has disclosed five vulnerabilities that he responsibly reported to Palo Alto Networks, affecting GlobalProtect, the VPN and endpoint agent used across thousands…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability in Oracle HTTP Server to its Known Exploited Vulnerabilities (KEV) Catalog after…
The Trusted Computing Group has published requirements that spell out what a Trusted Platform Module has to do before anyone calls it quantum-safe. A TPM…