Keymous+ Hacker Group Claims Responsibility for Over 700 Global DDoS Attacks
A shadowy group known as Keymous+ has emerged as a formidable force in the cyber landscape, claiming responsibility for over 700 Distributed Denial of Service…
A shadowy group known as Keymous+ has emerged as a formidable force in the cyber landscape, claiming responsibility for over 700 Distributed Denial of Service…
In a report published by ANSSI on July 1, 2025, the French cybersecurity agency revealed a highly skilled cybercrime group, dubbed Houken, has carried out…
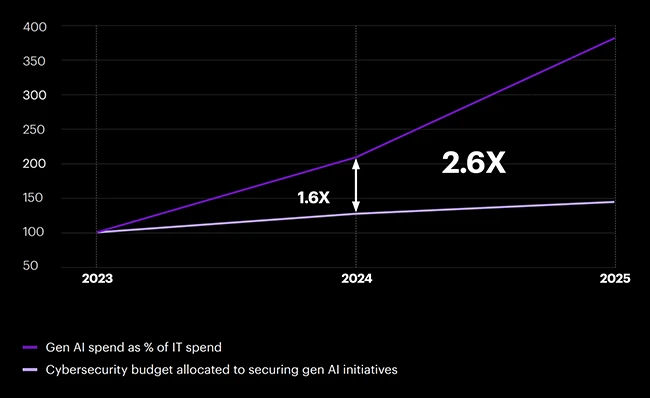
As AI reshapes business, 90% of organizations are not adequately prepared to secure their AI-driven future, according to a new report from Accenture. Globally, 63%…
Kelly Benefits data breach has impacted 550,000 people, and the situation continues to worsen as the investigation progresses Pierluigi Paganini July 03, 2025 A data…
The US government has taken another significant step towards strengthening cloud security with the release of CISA’s Binding Operational Directive (BOD) 25-01. Aimed at improving…
A newly disclosed vulnerability in Apache Seata, a popular open-source distributed transaction solution, has raised security concerns for organizations relying on affected versions. The flaw,…
Once upon a time, say, 2016, Ethereum was a curious new arrival in the crypto space. It promised more than digital gold. It whispered of…
In this Help Net Security interview, Henry Jiang, CISO at Ensora Health, discusses what it really takes to make DevSecOps work in healthcare. He explains…
The weaponization of Windows shortcut (LNK) files for malware distribution has increased by an astounding 50%, according to telemetry data, with dangerous samples rising from…
StealthCores launched StealthMACsec, a comprehensive IEEE 802.1AE compliant MACsec engine that brings advanced side-channel countermeasures to Ethernet network security. Building on the proven security foundation…
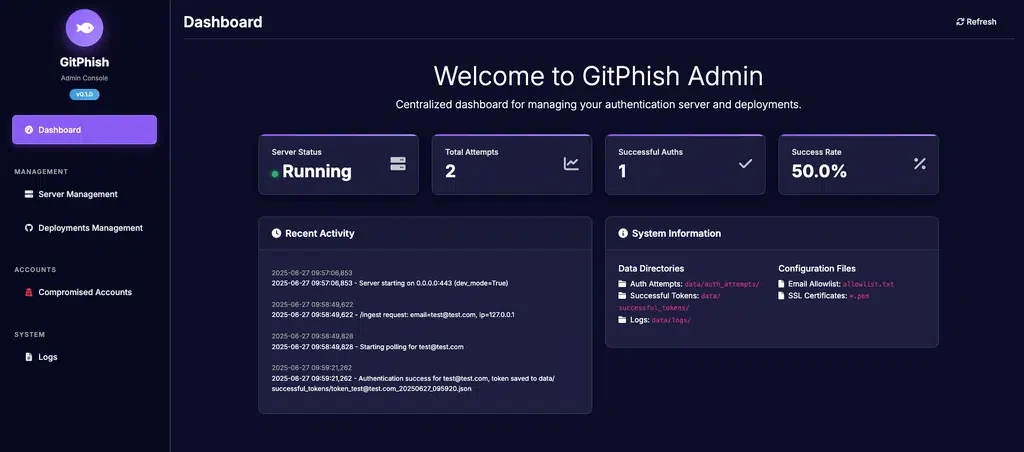
GitPhish is an open-source security research tool built to replicate GitHub’s device code authentication flow. It features three core operating modes: an authentication server, automated…
A newly disclosed vulnerability in ModSecurity, a widely used open-source web application firewall (WAF), exposes servers to denial-of-service (DoS) attacks by exploiting a flaw in…