Security Researchers Warn a Widely Used Open Source Tool Poses a ‘Persistent’ Risk to the US
“Nation states take on a strategic positioning,” says George Barnes, a former deputy director at the National Security Agency, who spent 36 years at the…
“Nation states take on a strategic positioning,” says George Barnes, a former deputy director at the National Security Agency, who spent 36 years at the…
Cybersecurity researchers are raising alarms as hackers increasingly weaponize email input fields to execute cross-site scripting (XSS) and server-side request forgery (SSRF) attacks. These vulnerabilities, often overlooked in web…
Regular User Access Reviews are required for regulatory compliance with standards such as SOX, HIPAA, GLBA, PCI, NYDFS, NYSDOH, and SOC 2. Additionally, increasing numbers…
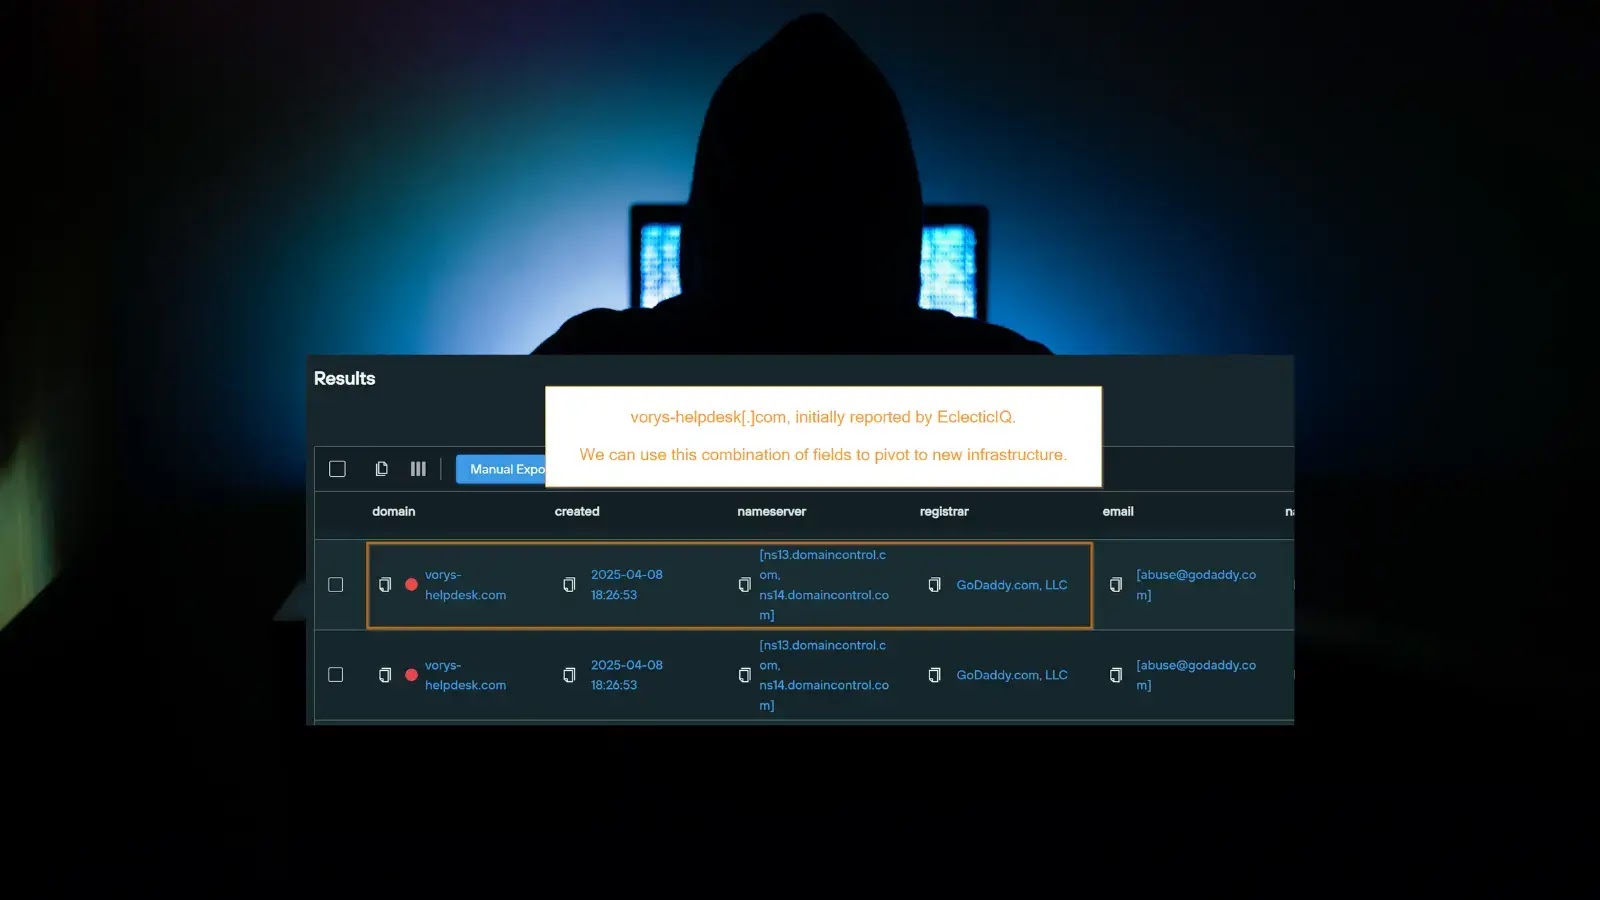
A recent investigation by cybersecurity firm EclecticIQ, in collaboration with threat hunters, has exposed a surge in malicious activity tied to the Luna Moth hacking…
A critical new attack chain, dubbed “SonicBoom,” that enables remote attackers to bypass authentication and seize administrative control over enterprise appliances, including SonicWall Secure Mobile…
A researcher has unveiled a novel integration between AI-powered Copilot and Microsoft’s WinDbg, dramatically simplifying Windows crash dump analysis. For decades, debugging Windows crash dumps…
A critical security vulnerability in Webmin, a widely-used web-based system administration tool, has been discovered, allowing remote attackers to escalate privileges and execute code with…
Cybersecurity researchers have uncovered a dangerous new exploitation technique, dubbed the “SonicBoom Attack Chain,” which allows hackers to bypass authentication and seize administrative control over…
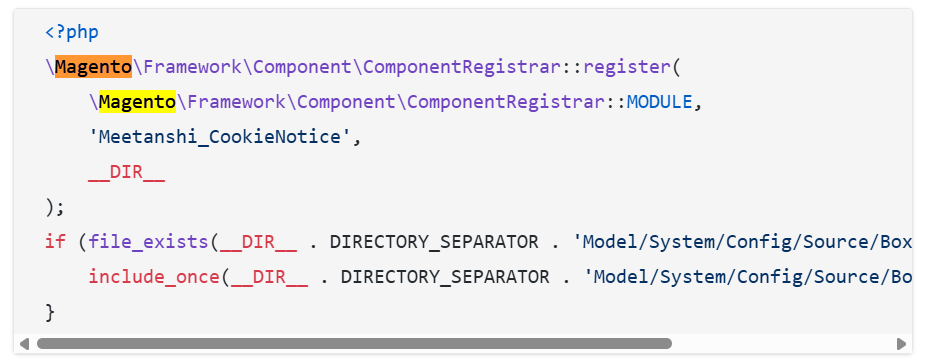
Sansec uncovered a supply chain attack via 21 backdoored Magento extensions Pierluigi Paganini May 05, 2025 Supply chain attack via 21 backdoored Magento extensions hit…
In a notable development that will affect numerous businesses globally, Microsoft has announced that it will commence the rejection of emails that do not adhere…
Over the past two weeks, media outlets have been rife with speculations about a significant cyber attack affecting three major UK-based companies: Marks & Spencer,…
Effective Vulnerability Management offers a view of a key part of cybersecurity, showing how practices, tools, and processes can help organizations reduce risk. About the…