Critical RCE Bug Rated 9.9 CVSS in Backup & Replication
Jun 18, 2025Ravie LakshmananVulnerability / Data Protection Veeam has rolled out patches to contain a critical security flaw impacting its Backup & Replication software that…
Jun 18, 2025Ravie LakshmananVulnerability / Data Protection Veeam has rolled out patches to contain a critical security flaw impacting its Backup & Replication software that…
Two critical vulnerabilities have been discovered in Citrix NetScaler ADC (formerly Citrix ADC) and NetScaler Gateway (formerly Citrix Gateway), potentially exposing sensitive data to hackers…
As applications become more distributed, traditional monitoring and security tools are failing to keep pace. This article explores how eBPF, when utilized by the graduated…
The roll-out of generative AI and agents will reduce Amazon’s total corporate workforce in the next few years, Andy Jassy, CEO of the online retailer,…
Veeam, a leading provider of data protection and backup solutions, disclosed three critical vulnerabilities affecting its widely deployed backup software. These flaws—assigned CVE-2025-23121, CVE-2025-24286, and…
This article showcases free, open-source security tools that support your organization’s teams in red teaming, threat hunting, incident response, vulnerability scanning, and cloud security. Autorize:…
Schneider Electric is reengineering its supply chain and supporting customers to operate more efficiently and sustainably. By focusing on the top 1,000 suppliers – responsible…
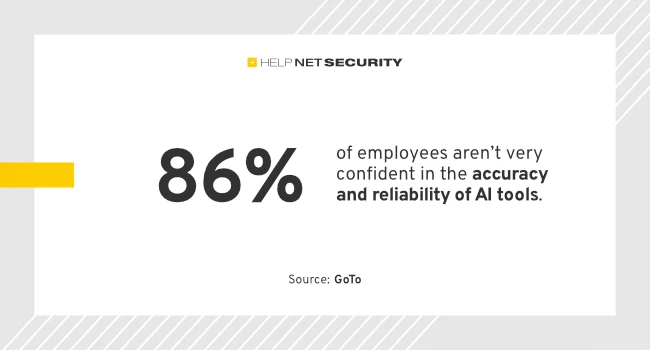
Despite widespread anticipation about AI’s positive impact on workforce productivity, most employees feel they were overpromised on its potential, according to GoTo. In fact, 62%…
In partnership with Schneider, Datacom helps customers drive sustainable change using EcoStruxure IT Expert. This platform provides full visibility of physical infrastructure, enabling precise tracking…
The world has shifted. Threat actors spend less time exploiting vulnerabilities and more time logging in using stolen credentials. This makes it difficult to detect…
The Qualys Threat Research Unit has discovered two linked local privilege escalation flaws. The first (CVE-2025-6018) resides in the PAM configuration of openSUSE Leap 15…
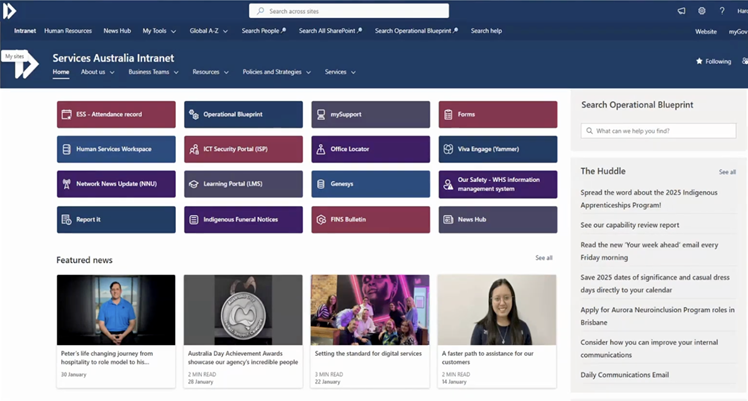
Services Australia is looking to relaunch its M365 SharePoint-based intranet in mid-July, hoping to re-establish it as “the main source of truth” for operational information…