Hackers Selling SS7 0-Day Exploit on Dark Web for $5,000
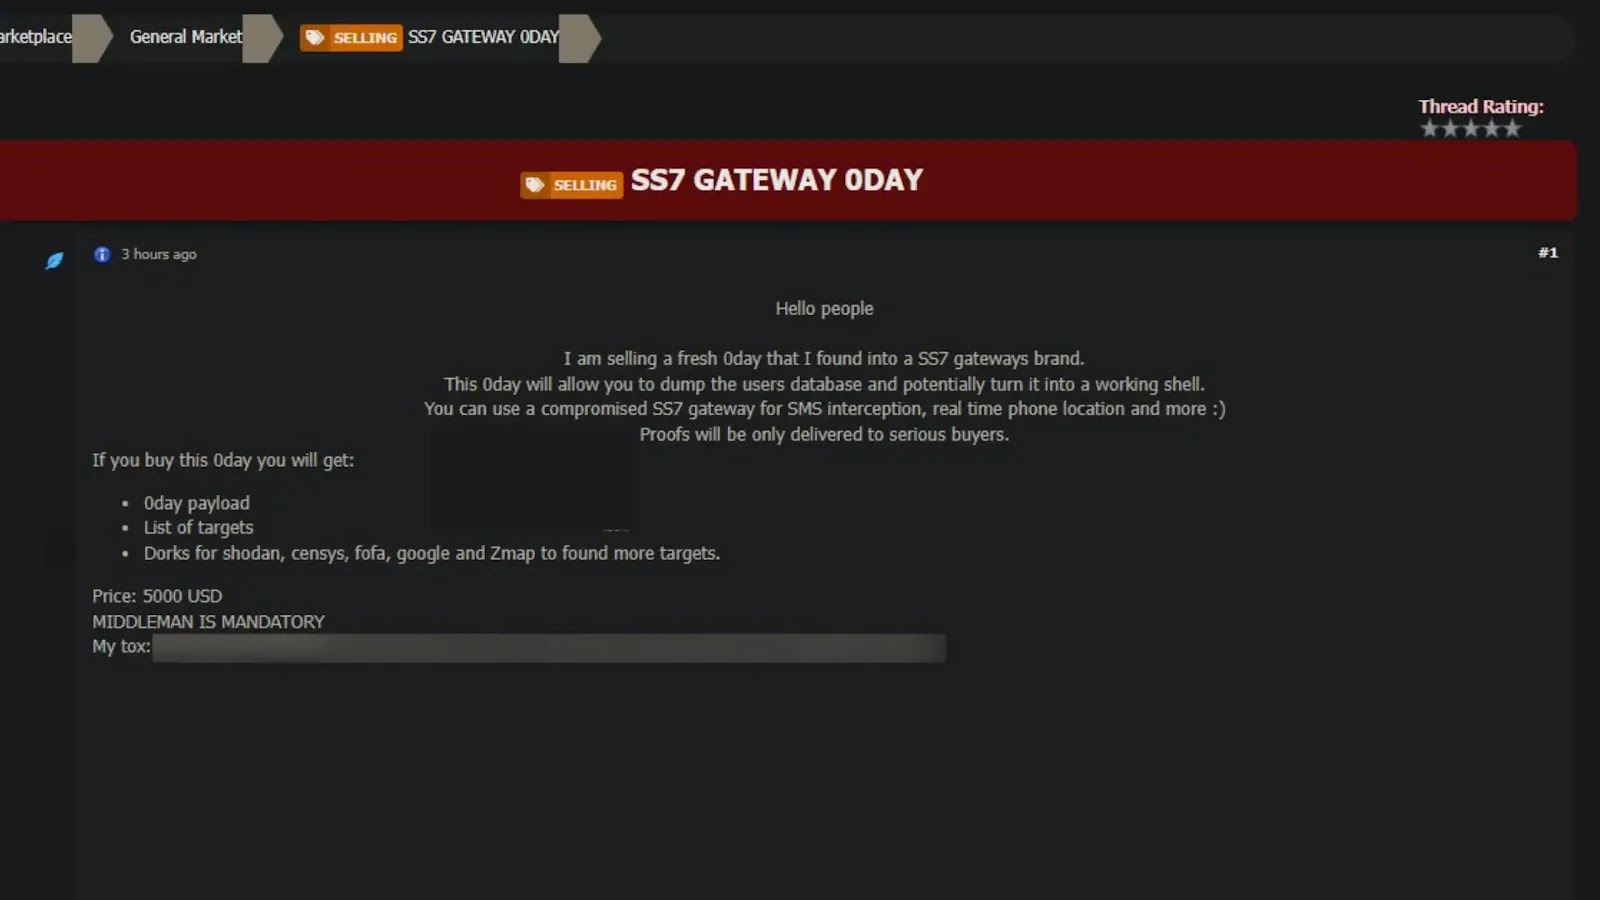
A newly discovered dark web listing claims to sell a critical SS7 protocol exploit for $5,000, raising alarms about global telecom security. The seller, operating…
A newly discovered dark web listing claims to sell a critical SS7 protocol exploit for $5,000, raising alarms about global telecom security. The seller, operating…
TeleMessage, an Israeli company that sells an unofficial Signal message archiving tool used by some U.S. government officials, has suspended all services after reportedly being…
The LUMMAC.V2 infostealer malware, also known as Lumma or Lummastealer, has emerged as a significant threat, employing the cunning “ClickFix” social engineering technique to compromise…
May 05, 2025Ravie LakshmananVulnerability / Zero-Day The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a maximum-severity security flaw impacting Commvault Command Center to…
The Seqrite Labs APT team has uncovered a sophisticated cyber campaign by the Pakistan-linked Transparent Tribe (APT36) targeting Indian Government and Defense personnel. This operation,…
May 05, 2025Ravie LakshmananNetwork Security / Vulnerability Cybersecurity researchers have disclosed a series of now-patched security vulnerabilities in Apple’s AirPlay protocol that, if successfully exploited,…
Kelly Benefits December data breach impacted over 400,000 individuals Pierluigi Paganini May 05, 2025 Kelly Benefits has determined that the impact of the recently disclosed…
Federal prosecutors indicted a man believed to be living in Yemen with deploying ransomware against multiple U.S. and global organizations. Rami Khaled Ahmed, 36, allegedly…
The Darcula phishing-as-a-service (PhaaS) platform stole 884,000 credit cards from 13 million clicks on malicious links sent via text messages to targets worldwide. The cyber…
The financially motivated threat group Venom Spider, also tracked as TA4557, has shifted its focus to corporate Human Resources (HR) departments with a highly targeted…
Cybersecurity firm Sansec has uncovered a sophisticated supply chain attack that has compromised 21 popular e-commerce applications, granting hackers full control over hundreds of online…
ESET has discovered Spellbinder, a new tool used by the China-linked cyber espionage group TheWizards to conduct AitM attacks and spread their WizardNet backdoor via…