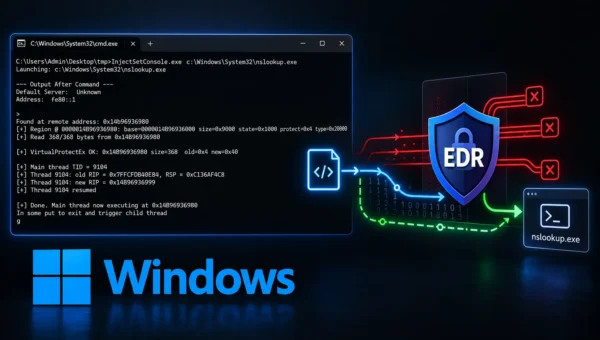
New Windows Process Injection Attack Evades EDR Monitoring Without WriteProcessMemory
A Windows process injection method disclosed by security researcher Two Seven One Three sidesteps two APIs closely associated with remote code injection: VirtualAllocEx and WriteProcessMemory.…