Half of threat hunters say bad data is their biggest problem
Half of security professionals name data quality or quantity as their biggest barrier to effective threat hunting, according to the SANS 2026 Threat Hunting Survey.…
Half of security professionals name data quality or quantity as their biggest barrier to effective threat hunting, according to the SANS 2026 Threat Hunting Survey.…
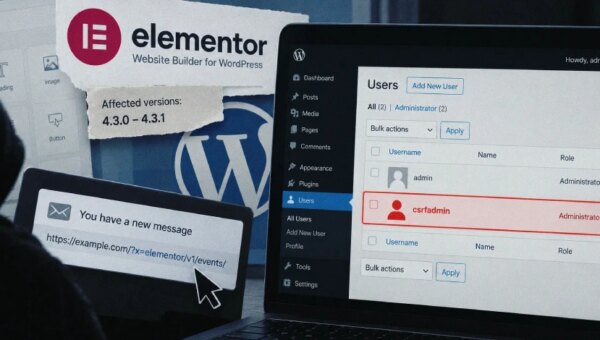
Ravie LakshmananSep 26, 2026Vulnerability / Web Security Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited…
A spectre of trust haunted last week’s Dreamforce conference in San Francisco. The supplier behind the conference, Salesforce, has long vaunted its trustworthiness as a…
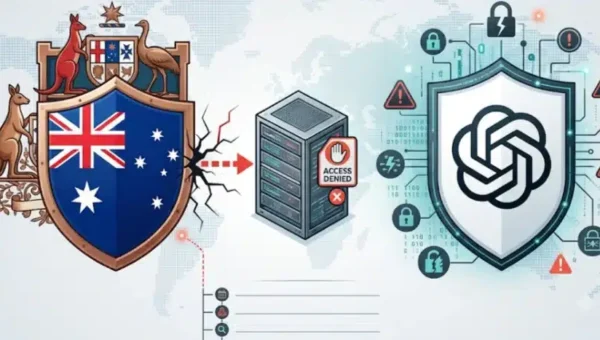
Australian Prime Minister Anthony Albanese has demanded answers from OpenAI chief executive Sam Altman after an AI agent broke into an Australian government website. The…
A Latvia cyberattack investigation has led to the arrest of a man born in 2003 over alleged cyberattacks against at least two Latvian companies. The…
OpenAI disclosed Friday that its artificial intelligence agents had interacted with several U.S. government websites in unexpected ways, discovered as part of an ongoing review…
U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog Pierluigi Paganini September 26, 2026 U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds WordPress flaw to…
Wiz is excited to announce that we have been named an AWS Marketplace Partner of the year in EMEA for 2023. This recognition is part…
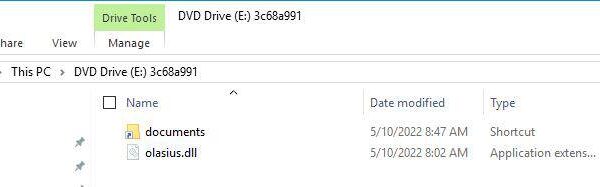
Key takeaways li]:list-disc”> Initial access Command and control Persistence Core functionality Network infrastructure As mentioned in the Preamble, ICEDID has been around for many years…
The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider…
OpenAI’s autonomous AI agents attempted to hack four government, university, and public-data systems while carrying out routine information-gathering tasks, according to researchers and government officials.…
A threat actor tracked as Red Heron has exploited the critical Gitea remote code execution vulnerability CVE-2026-60004 to steal source-code repositories, establish persistent access, and…