Are threat feeds masking your biggest security blind spot?
Security teams that subscribe to threat feeds get lists of known malicious domains, IPs, and file signatures that they can leverage to blacklist and prevent…
Security teams that subscribe to threat feeds get lists of known malicious domains, IPs, and file signatures that they can leverage to blacklist and prevent…
In this Help Net Security interview, Dan Lohrmann, CISO at Presidio, discusses the need for organizations to rethink their leadership and operational strategies and the…
Versent is excited to announce it is a recipient of a 2024 Geography and Global AWS Partner Award, recognising leaders around the globe that are…
In 2024, ransomware remained the top cybersecurity threat to organizations worldwide. New groups filled the void left by law enforcement crackdowns, targeting businesses with record-breaking…
US authorities are considering a ban on TP-Link routers due to concerns over their potential role in Chinese cyber attacks. The popular router manufacturer, which…
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a stark warning to senior government officials and political figures to adopt end-to-end encrypted messaging services…
Some companies have been using AI as a data analytics tool for years, but most companies are now rushing to embrace generative AI – a cloud-based…
As Australian households continue to embrace high-speed internet, a reliable and fast Wi-Fi network has become essential, especially for large homes or multi-story spaces. With…
NSW Department of Customer Service is looking to the multilingual capabilities of generative AI for more accessible and inclusive public access to information and services. …
An ongoing phishing scam is abusing Google Calendar invites and Google Drawings pages to steal credentials while bypassing spam filters. According to Check Point, which…
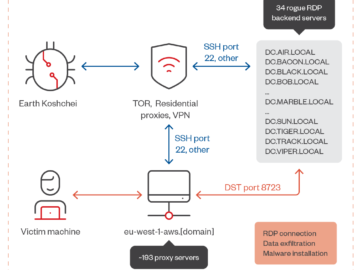
Russia-linked APT29 group used red team tools in rogue RDP attacks Pierluigi Paganini December 18, 2024 Russia-linked APT29 group uses malicious RDP configuration files, adapting…
The Russian hacking group tracked as APT29 (aka “Midnight Blizzard”) is using a network of 193 remote desktop protocol proxy servers to perform man-in-the-middle (MiTM) attacks…