ConnectOnCall breach exposes health data of over 910,000 patients
Healthcare software as a service (SaaS) company Phreesia is notifying over 910,000 people that their personal and health data was exposed in a May breach…
Healthcare software as a service (SaaS) company Phreesia is notifying over 910,000 people that their personal and health data was exposed in a May breach…
In a significant move that will reshape the cybersecurity landscape, Arctic Wolf and BlackBerry Limited (NYSE: BB; TSX:BB) announced today that they have entered into…
Bulletproof hosting services, a type of dark internet service provider, offer infrastructure to cybercriminals, facilitating malicious activities like malware distribution, hacking attacks, fraudulent websites, and…
This week on the Lock and Code podcast… Privacy is many things for many people. For the teenager suffering from a bad breakup, privacy is…
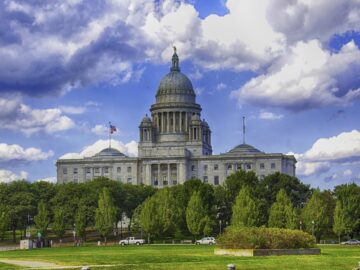
Rhode Island State House (Image: MOHANN) Rhode Island is warning that its RIBridges system, managed by Deloitte, suffered a data breach exposing residents’ personal information after the…
Researchers have discovered a new Android banking trojan targeting Indian users, and this malware disguises itself as essential utility services to trick users into providing…
CoinLurker is a sophisticated data-stealing malware that has revolutionized fake update campaigns. Written in the Go programming language, CoinLurker incorporates advanced obfuscation and anti-analysis techniques,…
Researchers discovered multiple vulnerabilities in Ruijie Networks’ cloud-connected devices. By exploiting these vulnerabilities, attackers can remotely compromise access points, gain unauthorized access to internal networks,…
SUMMARY Arrest and Charges: Baron Martin, 20, arrested for producing child sexual abuse material and cyberstalking, linked to extremist networks 764 and CVLT. Disturbing Crimes:…
While malware attacks embedded in games have been a longstanding cybersecurity concern, a more sinister threat has emerged. Researchers have uncovered a disturbing new tactic:…
A threat actor tracked as MUT-1244 by DataDog researchers has been targeting academics, pentesters, red teamers, security researchers, as well as other threat actors, in…
Dec 16, 2024Ravie LakshmananMalvertising / Threat Intelligence Cybersecurity researchers have shed light on a previously undocumented aspect associated with ClickFix-style attacks that hinge on taking…