It’s Time To Untangle the SaaS Ball of Yarn
It’s no great revelation to say that SaaS applications have changed the way we operate, both in our personal and professional lives. We routinely rely…
It’s no great revelation to say that SaaS applications have changed the way we operate, both in our personal and professional lives. We routinely rely…
A recent discovery by Miggo Research has unveiled a critical configuration vulnerability in Amazon Web Services (AWS) that exposes thousands of web applications to potential…
ALBeast is a critical vulnerability that allows attackers to bypass authentication and authorization in AWS ALB-based applications. Learn how to mitigate this risk and protect…
In recent years, the landscape of cybersecurity threats has evolved, with attackers constantly refining their techniques to exploit vulnerabilities in increasingly sophisticated ways. Among the…
RightCrowd introduced Mobile Credential Management feature for RightCrowd SmartAccess. This solution transforms how organizations manage and control access, replacing traditional methods with a more secure,…
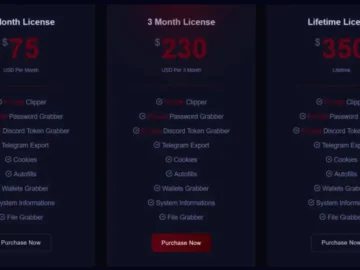
A new malware strain called Styx Stealer has emerged, posing a significant threat to online security. Discovered in April 2024, Styx Stealer malware targets popular…
Iranian threat actor TA453 launched a phishing campaign targeting a prominent religious figure with a fake podcast invitation aiming to deliver a new malware toolkit,…
Last week, a cybercriminal using the handle ZeroSevenGroup dumped 240GB of data on the infamous stolen data site BreachForums, that they said came from a…
US bank Wells Fargo has reported a big jump in recommendations from customers after using artificial intelligence (AI) and automation to help families manage the…
BMCs are specialized microcontrollers embedded in servers and other devices, responsible for monitoring and managing hardware health, including temperature, voltage, and system logs. Cybersecurity researchers…
The Post Office has revealed a disconnect between branch systems and a Fujitsu datacentre is what left subpostmasters unable to authenticate and log onto their…
Cybersecurity researchers at Symantec recently identified a new malware that exploits a PHP vulnerability(CVE-2024-4577) in the CGI argument injection flaw. This vulnerability affects all versions…