ATO culture keeps a cap on agentic AI ambitions
Key points The ATO believes agentic AI might only be needed for a small portion of an end-to-end process, with re-engineering, automation and machine learning…
Key points The ATO believes agentic AI might only be needed for a small portion of an end-to-end process, with re-engineering, automation and machine learning…
F5 and CISA on Tuesday warned organizations that threat actors have been exploiting a critical-severity BIG-IP Access Policy Manager (APM) vulnerability as a zero-day. The…
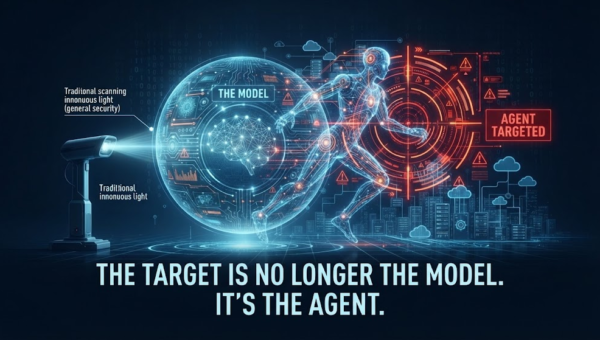
The Target Is No Longer the Model. It’s the Agent. Pierluigi Paganini September 21, 2026 AI agents are becoming the new attack surface, exposed to…
I think the biggest thing that’s going to give attackers the advantage over defenders in this AI race is the fact that defenders are embedded…
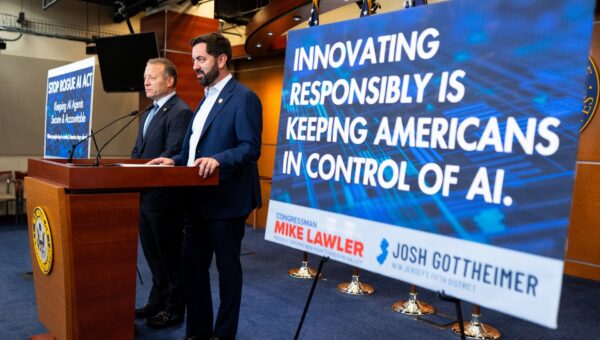
A House Democrat tapped to lead his party’s efforts on artificial intelligence has introduced legislation that would establish a test program within the Cybersecurity and…
Cloudflare and Microsoft say they have taken part in a coordinated effort with law enforcement partners to disrupt “EvilTokens”, a phishing-as-a-service operation designed to bypass…
“EvilTokens uses tailored phishing messages to trick victims into authorizing attacker access through Microsoft’s legitimate sign-in process,” explained Jason Rivera, global field CISO at cyber…
We recently announced AI Security Posture Management (AI-SPM), which provides AI security capabilities that empower AI developers and data scientists to build with AI while…
As the threat landscape continues to evolve, cybersecurity stakes are growing exponentially higher for today’s organizations. Between Log4j, geopolitical tension, and increasing ransomware threats, security…
Sweden’s data privacy regulator, IMY, has imposed a $183,000 (SEK 1.8 million) fine on IT systems provider Miljödata for inadequate security measures leading to a…
F5 has warned that hackers are actively exploiting a critical zero-day vulnerability in BIG-IP Access Policy Manager (APM) deployments to execute code remotely without authentication.…
A newly discovered privilege escalation flaw in Veeam Agent for Microsoft Windows could allow attackers with local access to compromised endpoints to execute commands as…