Microsoft quietly fixes Windows troubleshooter privesc vulnerability
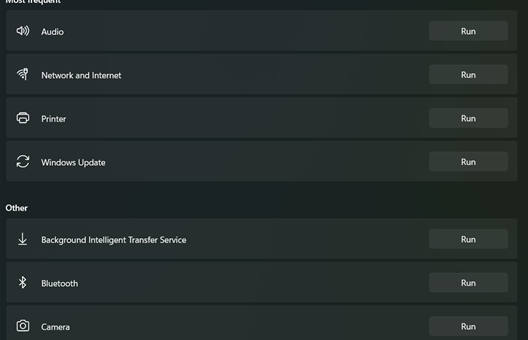
Key points A Windows 11 Get Help flaw let standard users exploit DiagSvc to gain full SYSTEM control, and Microsoft fixed it quietly without issuing…
Key points A Windows 11 Get Help flaw let standard users exploit DiagSvc to gain full SYSTEM control, and Microsoft fixed it quietly without issuing…
SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 6 Pierluigi Paganini November 01, 2026 Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on…
A federal judge dismissed a lawsuit from the federal government seeking to preemptively block Democratic Senate candidate Mary Peltola from assuming office if she wins…
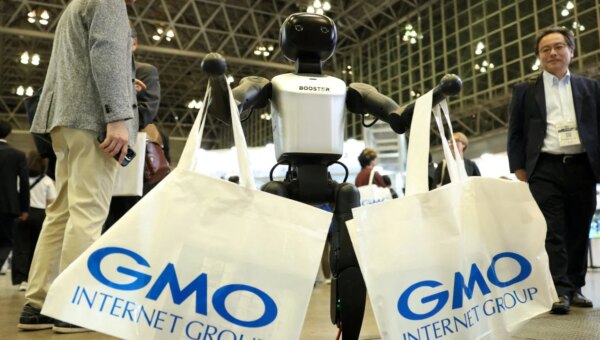
An analysis by Japan’s GMO Internet Group found that a North Korea-linked hacking group was likely behind the cyberattack on the company last month, sources…
A new exploit method, referred to as OWASSRF, has been discovered by researchers and exploited in the wild. This exploit combines CVE-2022-41080 and CVE-2022-41082 to…
Ravie LakshmananNov 01, 2026Windows Security / Cyber Espionage Cybersecurity researchers have disclosed details of what has been described as a “highly sophisticated infection chain” targeting…
Key points China-linked group VAPOR PANDA used the open-source ARTEX framework to target more than 200 organisations worldwide in under a fortnight, CrowdStrike said. ARTEX…
FBI Blames North Korea for $6 Billion Binance Crypto Theft Pierluigi Paganini November 01, 2026 The FBI blames North Korea for stealing $6 billion from…
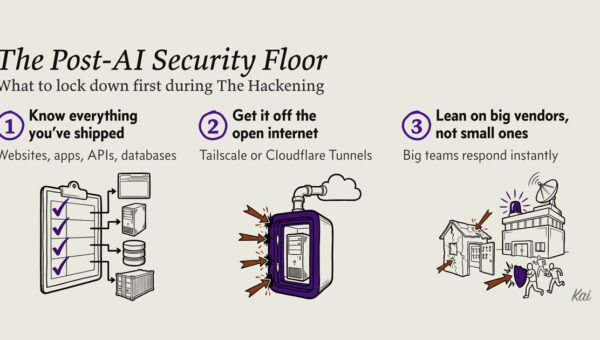
Cybersecurity recommendations during The Hackening. In 2023 I guessed that AI would help attackers before it helped defenders, and that their lead would last three…
A critical remote code execution vulnerability (CVE-2022-47939) has been identified in the ksmbd module of the Linux kernel. This means that remote attackers could potentially…
The FBI has confirmed that North Korean state-sponsored hackers known as TraderTraitor were behind the $6.3 billion crypto-theft attack on Binance, making it the largest…
Chainalysis has confirmed that an attacker used “offensive agentic techniques” to access its systems and internal tools, exposing customer account details. The blockchain investigation company…