
Avoiding FALSE POSITIVE REPORTS in bug bounty

Source link
Related Articles
All Mix →
Hack My Career: Saskia Braucher
When Saskia joined the tech world, she didn’t follow the conventional path of computer science degrees or coding boot camps. Instead, her journey was shaped…
Live-hacking Dropbox in Amsterdam for H1-3120
Nearly 40 hackers representing 12 countries were in Amsterdam on May 26, 2018 with one focus: hacking Dropbox! Dropbox runs a top public bug bounty…
API Security’s Role in Responsible AI Deployment
Table of Contents Understanding APIs in AI Systems API Security's Role in Responsible AI Deployment Best Practices for API Security in AI Systems Strong Authentication…
a Hacker’s Backdoor: Service Control Manager
a Hacker’s Backdoor: Service Control Manager Source link
Hacker101 CTF++: Find flags, get private bug bounty program invitations
Table of Contents Hacker101 CTF++ Groups HackerOne SSO and Private Bug Bounty Program Invitations Hacker101 CTF++ Three months ago, we introduced the Hacker101 CTF: A…
Assign Severity Ratings on Custom Policies
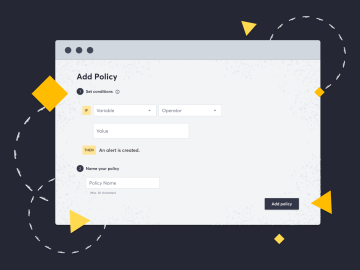
Table of Contents Why would I use severity ratings with Attack Surface Custom Policies? Setting rules on fingerprinted technologies now possible “As part of our…