
Broken Access Control – Lab #10 User ID controlled by param with password disclosure | Long Version

Source link
Related Articles
All Mix →
Case study: How Burp AT helped expose whistleblower reports via a critical vulnerability that was overlooked for years | Blog
Table of Contents The dilemma of timeboxed engagements Agentic AI meets human-led pentesting From academic finding to confirmed exploit The vulns that get away Pairing…
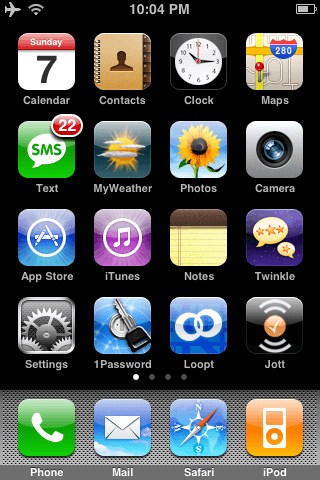
How I Organize My iPhone Applications
Table of Contents 1. Primary Applications 2. Secondary Applications 3. Specialized or Niche Applications 4. Unused Apple Applications and Games It can be frustrating to…
Advent of Cyber 2022: Day 17 Filtering for Order Amidst Chaos (Walkthrough)
Advent of Cyber 2022: Day 17 Filtering for Order Amidst Chaos (Walkthrough) Source link
Clearing Up The Terminology — API Security
Table of Contents What does an AI gateway do? What does an AI firewall do? What does an AI Control Platform do? Side by side…
2020 Hacker Community Year in Review
Hackers are no stranger to finding creative ways to overcome obstacles, and 2020 presented numerous challenges for them to conquer. At HackerOne, we strive to…

Easy and secure Credential Management
Earlier this year we introduced Hacker Email Aliases which enables you to secure set up accounts for hackers inside your program, but to make it…