
Broken Access Control – Lab #10 User ID controlled by param with password disclosure | Short Version

Source link
Related Articles
All Mix →
Bug Bytes #203 – CVSS 4.0, MOVEIt and How CI/CD Pipelines Go Wrong
Bug Bytes is a weekly newsletter curated by members of the bug bounty community. The second series is curated by InsiderPhD. Every week, she keeps…

Intigriti Bug Bytes #235 – April 2026
Table of Contents Blogs & videos BugQuest 2026: 31 Days of Broken Access Control Tools Fuzzing with multiple content types Intigriti's first Ambassador Bug Bounty meetup…
Replacing Cursor With Neovim and Claude Code
Table of Contents Ghostty to the rescue The Ghostty Keybindings The result My three-paned Ghostty / Neovim / Claude Code Setup (click for full size)…
Extreme Transparency or Corporate Security Responsibility?
Extreme Transparency or Corporate Security Responsibility? Source link
How Human Testers Improve Application Security
A suite of DevSecOps tools is available to automate reviews, audits, tests, and scans throughout the development pipeline, which have become standard in application security…
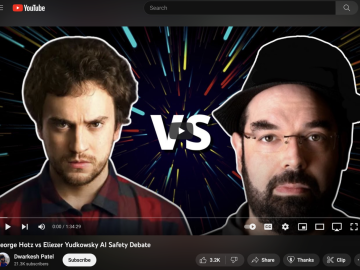
Thoughts on the Eliezer vs. Hotz AI Safety Debate
Table of Contents How I’d characterize and address each of their positions Hotz’ arguments Yudkowski’s arguments A realistic scenario Here’s how I wish these debates…