
Broken Access Control – Lab #9 UID controlled by param with data leakage in redirect | Long Version

Source link
Related Articles
All Mix →
AWS S3 Misconfiguration Explained – And How To Fix It
Table of Contents How it is done What can happen How to fix it Test if you are vulnerable with Detectify A technical write-up explaining…
Hunting Down The Top 5 Most Common Price Manipulation Vulnerabilities in E-Commerce Websites
Table of Contents The 5 most common price manipulation vulnerabilities 1) Formula injection: price tampering 2) Formula injection: quantity tampering 3) Integer overflow 4) Coupons:…
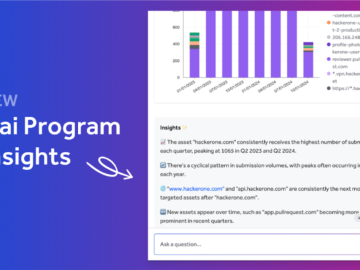
Hai’s Latest Evolution: Intelligence, Context, and More Intuitive UX
Table of Contents Transforming Security Program Management: A Day with Hai 1. Hai Program Insights: Instantly Understand Your Programs 2. Contextual Conversation When It Matters…
HackerOne Professional Free For Open Source Projects
Here at HackerOne, open source runs through our veins. Our company, product, and approach is built-on, inspired by, and driven by open source and a…
EU-FOSSA 2 Open Source Bug Bounty Programme Series | Q&A
Following the success of the European Commission’s pilot bug bounty programme with HackerOne last year, they are announcing the launch of a new bug bounty…
Attacking LLM – Prompt Injection
Attacking LLM – Prompt Injection Source link