Executive Summary
PHP2Shell’s fix is to update PHP, but patching at scale is slow. Only 199,000 of 156 million PHP installations were patched in the first 12 hours after disclosure. In the meantime, Qualys’s configuration-level mitigation reduces exposure to the confirmed attack path without code changes, with or without an agent. WAF, IPS, and EDR protections from major vendors add further layers, and TruConfirm shows which hosts are actually reachable: 25 of 1,539 in one customer environment. Soon, Qualys ETM will factor these controls into risk scores. These controls buy time, but patching remains the only complete fix.
PHP2Shell comes with a clear instruction: update PHP. Fixed releases exist for supported branches, and Qualys customers can identify PHP installations using network scans, Cloud Agents, container assessments, and Deep Scan where supported, while assessing exposed web applications and APIs with Qualys TotalAppSec. Patching at this scale still takes time. In Qualys telemetry, only 199,000 of the 156 million PHP package installations with a known version had been patched during the first 12 hours after disclosure.
Those first days are where mitigations and compensating controls earn their place. They reduce risk while updates roll out, and the right visibility shows which servers need attention first. Our PHP2Shell guide covers detection and fixed versions. Here is how to bridge the gap between disclosure and patch.
Start with Qualys Mitigation
Qualys provides a configuration-level mitigation for PHP2Shell based on PHP’s guidance and insights from the Qualys Threat Research Unit. It disables session upload progress and hardens related session-handling configuration on supported hosts. This reduces exposure to the confirmed session-lifecycle attack path without requiring application-code changes. It does not eliminate every exploitation path associated with the two CVEs. Applications that depend on upload-progress functionality should be tested after the change.
- Configuration-level, with restart verification. The mitigation applies configuration changes and automatically restarts the PHP service. Review the execution logs and restart the service manually if a restart is still required. Confirm that every affected PHP worker has picked up the new configuration.
- Verified, not assumed. After the restart, Qualys checks the effective configuration to confirm the setting is active and not overridden elsewhere.
- With or without an agent. Customers with vulnerable detections can select Mitigate Now from their dashboards. For appliances, DMZ servers, and legacy hosts that cannot run a Cloud Agent, the same mitigation script is available in the Custom Assessment and Remediation (CAR) library in TruRisk Eliminate and runs directly on scanner-based hosts.
- Ready when the patch is. You can deploy supported vendor patches through TruRisk Eliminate. Qualys reports a High patch reliability rating for these updates and no OS reboot requirement for this PHP package update. Restart every service that loads PHP and verify that its workers are running the patched build.
Mitigation reduces risk in the interim. Updating remains the only complete fix.
Add Layers from the Security Stack You Already Run
The tools already in your environment can work alongside the mitigation, each at a different point in the attack path.
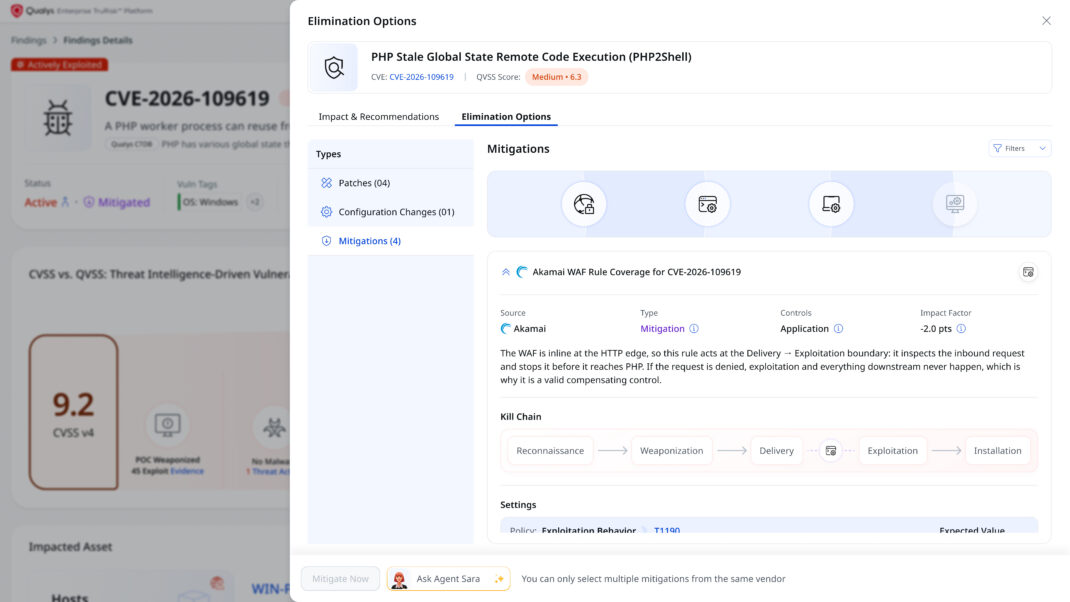
Network and application protection: WAF and IPS. Vendors including Akamai, Cloudflare, F5, Palo Alto Networks, Fortinet, and Check Point have published PHP2Shell protections. Coverage varies by product, CVE, signature, and configuration. These protections can block known exploit requests; some, including Cloudflare’s, also inspect and block malicious responses. Keep signatures current and confirm that the relevant traffic is inspected and blocking is enabled. Cloudflare has reported attempts to bypass its protections, so treat these controls as additional layers while patching proceeds.
After exploitation: EDR. Endpoint controls can provide visibility into suspicious child processes, malicious command execution, and web-shell deployment. CrowdStrike Falcon and Cortex XDR document PHP2Shell-related post-exploitation protections. For Microsoft Defender for Endpoint and other tools, verify the applicable platform support and enabled policies before claiming specific coverage.
These layers can detect or block different stages of an attack, but they do not guarantee that every exploitation attempt will be stopped.
Each layer catches what the one before it might miss.
PHP2Shell 3rd-party mitigation and compensating controls
Select the WAF, IPS, and EDR you run to see the exact signatures and policies each vendor has released for CVE-2026-109618 and CVE-2026-109619, ready to copy into your console.
Edge
WAF
None
Network
IPS
None
Host
EDR
None
Platform
This interactive view needs JavaScript. Signatures covering both CVEs: Akamai 3000991; Cloudflare seven managed rules; F5 BIG-IP 200204113, 200103697, 200204115; FortiWeb 1002017614, 1002017615; Palo Alto Networks 543004, 97622 to 97625; FortiGate 62657, 62658; Check Point CPAI-2026-15172, 15184, 15224; Trend Vision One 1012749, 1012754. Endpoint policies are listed for CrowdStrike Falcon, Microsoft Defender for Endpoint, Cortex XDR, SentinelOne and Cybereason.
Note: Rule and policy IDs are as published by each vendor in October 2026; confirm them in your console. The endpoint policies act after exploitation and are mapped to the attacker’s next step, not to the CVEs themselves, so verify each one fires for your PHP worker. Compensating controls reduce risk; updating PHP remains the only complete fix.
Give Your Controls Credit in Qualys ETM
Two servers can run the same unpatched PHP build and carry very different risk. One sits behind a WAF rule that names both CVEs, with EDR watching its web server process. The other faces the internet with nothing in front of it. A version-based check can report the same vulnerability on both assets, even though their exposure and compensating controls differ.
Qualys ETM is being extended to close that gap. It arrives in three steps:
- Recommendations on every finding. ETM will show which applicable third-party controls can reduce exposure for each vulnerability, so teams know what to enable and where.
- Controls reflected in the score. Controls that are in place will lower a finding’s QVSS score to reflect your actual defenses, shown as the Environmental score, so remediation queues focus on what still needs attention.
- Action from the same platform. Teams will be able to apply third-party mitigations through TruRisk Eliminate, from the platform that found the exposure.
Validate the Tested Entry Point with TruConfirm
TruConfirm helps validate indicators of the tested PHP2Shell entry point. According to Qualys’s PHP2Shell guide, its benign probe checks for behavior indicating that the entry point is reachable and the upload-progress mitigation is absent, without creating files, executing code, or applying memory pressure.
Qualys reports that, in one customer environment with 1,539 assets running PHP, TruConfirm returned positive validation results for 25 assets. These findings help prioritize investigation and remediation. A negative result does not establish that every exploitation path is closed. After mitigation or patching, repeat the validation and separately verify the effective configuration, installed packages, and running PHP workers.
Where to Start
- Use QID 45110 to support PHP discovery, then use the applicable vulnerability detection QIDs and software inventory to assess assets in scope.
- Use TruConfirm results alongside internet exposure and business criticality to prioritize remediation.
- Apply the supported Qualys mitigation workflow to systems awaiting an update, using agent-based or scanner-based execution as applicable.
- Verify the effective configuration and required restarts.Keep applicable WAF, IPS, and EDR protections enabled and current as additional layers.
- Deploy the appropriate PHP or vendor update, restart every service that loads PHP, verify the running patched build, and repeat the relevant validation checks.
Compensating controls buy valuable time, but they do not remove the flaw. Keep tracking every system until it is patched.
Not a Qualys customer yet? Sign up for the free PHP2Shell mitigation service.
Contributors
- Saeed Abbasi, Director, Product Management for Security Research, Qualys