Why AI raises the stakes for exposure validation
AI dominated the conversation at Fal.Con 2026, but one of the most important takeaways wasn’t simply how AI is changing cyber defense. It was how…
AI dominated the conversation at Fal.Con 2026, but one of the most important takeaways wasn’t simply how AI is changing cyber defense. It was how…
Enterprises that had been blocking the new Copilot address to prevent employees accessing their personal Microsoft accounts can use Microsoft’s TenantRestrictions control to achieve their…
AI convergence AI is causing previously distinct sectors such as ITSM and cybersecurity to converge, with AI itself turning into a unifying AIOps front end…
Run that comparison against your own data instead of against an industry average. A retail transaction log with a two-year retention window carries a different…
During that window, threat actors, whose ability to build exploit kits has been “wildly accelerated” by AI, likely had time to reverse engineer exploits from…
Attackers operate largely the same way. They scrape your org chart, guess who signs the wire, assume which domains belong to you and harvest what…
Compromise could expose the identity gateway The implications extend beyond the F5 appliance itself. “An attacker with access to BIG-IP APM can intercept SSO tokens…
A newly identified AI attack technique can let unauthenticated users trigger privileged workflows and access enterprise systems, highlighting a gap in how identity and access…
Require outputs to be grounded in authoritative sources and verify claims before acting. Introduce approval workflows and system checks. Log claims, evidence, and outcomes, and…
DAVID provides authorized users with access to extensive driver and vehicle information, meaning a successful intrusion can yield considerably more than a database full of…
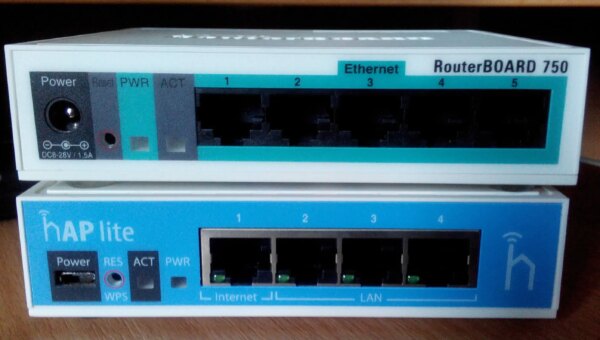
MikroTik released patches in RouterOS 7.25 beta 3, 7.24.2, 7.23.4, and 6.49.21 and advises against enabling the SSH service on the internet interface. Despite this…
A limited grant “narrows what any container-level leak can expose,” Handa said. She also recommended routing connected-app traffic through DLP or CASB inspection to catch…