Unremovable Spyware on Samsung Devices Comes Pre-installed on Galaxy Series Devices
Samsung has been accused of shipping budget Galaxy A and M series smartphones with pre-installed spyware that users can’t easily remove. The software in question,…
Samsung has been accused of shipping budget Galaxy A and M series smartphones with pre-installed spyware that users can’t easily remove. The software in question,…
A threat actor known as “888” has purportedly dumped sensitive data stolen from electronics giant LG Electronics, raising alarms in the cybersecurity community. The breach,…
AccuKnox, a global leader in Zero Trust Cloud-Native Application Protection Platforms(CNAPP), today announced its partnership with Alice Blue India, a prominent brokerage andfinancial services firm,…
A critical vulnerability allowing attackers to inject malicious code into Cursor’s embedded browser through compromised MCP (Model Context Protocol) servers. Unlike VS Code, Cursor lacks…
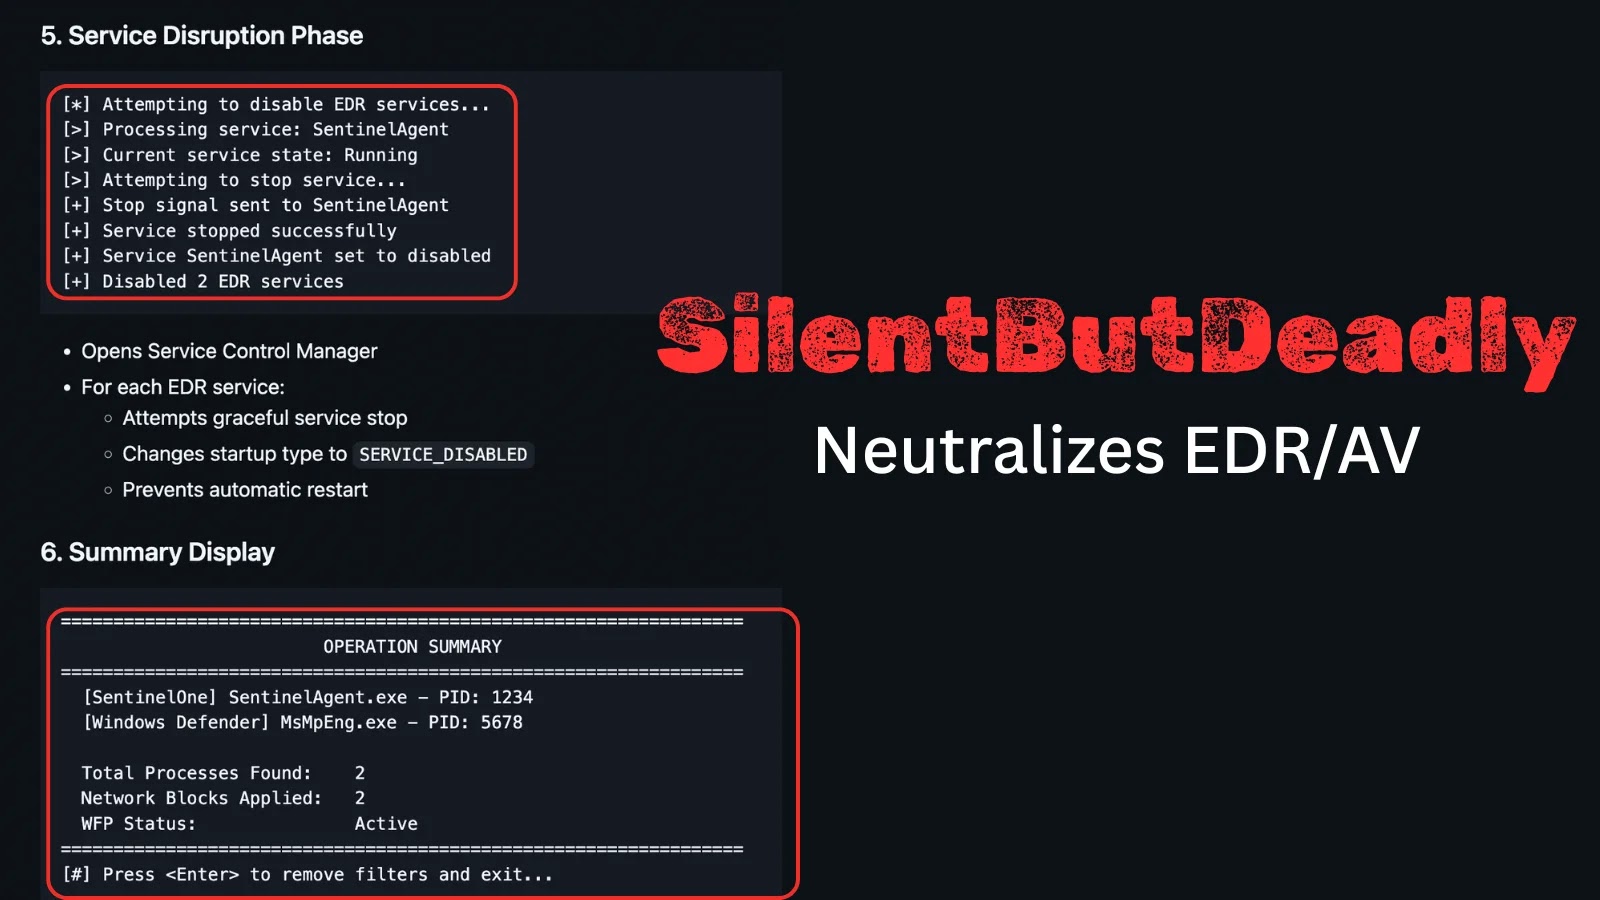
A new open-source tool called SilentButDeadly has emerged, designed to disrupt Endpoint Detection and Response (EDR) and antivirus (AV) software by severing their network communications.…
A serious security flaw in Cisco Catalyst Center Virtual Appliance has been discovered that allows attackers with low-level access to gain full administrator control over…
A proof-of-concept (PoC) exploit tool for CVE-2025-64446 has been publicly released on GitHub. This vulnerability, affecting FortiWeb devices from Fortinet, involves a critical path traversal…
A new threat targeting Chinese users has appeared with a dangerous ability to shut down security tools. RONINGLOADER, a multi-stage loader spreading a modified version…
A severe remote code execution (RCE) flaw has been uncovered in pgAdmin4, the popular open-source interface for PostgreSQL databases. Dubbed CVE-2025-12762, the vulnerability affects versions…
Chinese government-backed hackers used Anthropic’s Claude Code tool to carry out advanced spying on about thirty targets worldwide, successfully breaking into several major organizations. The…
Attackers are using fake invoice emails to spread XWorm, a remote-access trojan that quietly steals login credentials, passwords, and sensitive files from infected computers. When…
A new malware family targeting macOS systems has emerged with advanced detection evasion techniques and multi-stage attack chains. Named DigitStealer, this information stealer uses multiple…