5 Immediate Steps to be Followed After Clicking on a Malicious Link
Clicking on a malicious link can quickly turn your device into a security risk. Just seconds after clicking, your browser might start downloading malware, taking…
Clicking on a malicious link can quickly turn your device into a security risk. Just seconds after clicking, your browser might start downloading malware, taking…
A massive, coordinated botnet campaign is actively targeting Remote Desktop Protocol (RDP) services across the United States. Security firm GreyNoise reported on October 8, 2025,…
Along with the release of Kali Linux 2025.3, a major update introduces an innovative tool that combines artificial intelligence and cybersecurity: the llm-tools-nmap. A new experimental…
Threat actors have reemerged in mid-2025 leveraging previously disclosed vulnerabilities in SonicWall SSL VPN appliances to deploy Akira ransomware on enterprise networks. Beginning in July,…
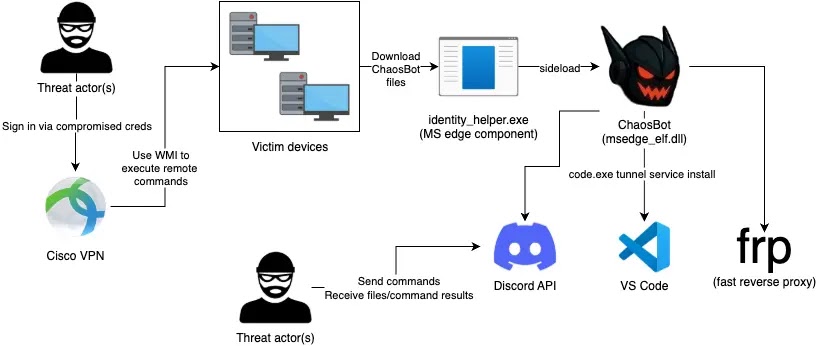
ChaosBot surfaced in late September 2025 as a sophisticated Rust-based backdoor targeting enterprise networks. Initial investigations revealed that threat actors gained entry by exploiting compromised…
Menlo Park, USA, October 10th, 2025, CyberNewsWire AccuKnox, a leader in Zero Trust Cloud Native Application Protection Platforms (CNAPP), is proud to announce that Nanoprecise…
Socket’s Threat Research Team has uncovered a sophisticated phishing campaign involving 175 malicious npm packages that collectively accumulated over 26,000 downloads. The campaign, dubbed “Beamglea”…
Since its emergence in early 2025, RondoDox has rapidly become one of the most pervasive IoT-focused botnets in operation, targeting a wide range of network-connected…
Microsoft Defender for Endpoint is incorrectly flagging specific versions of SQL Server as having reached their end-of-life, causing potential confusion for system administrators. The issue,…
A critical vulnerability in GitHub Copilot Chat, rated 9.6 on the CVSS scale, could have allowed attackers to exfiltrate source code and secrets from private…
An active in-the-wild exploitation of a zero-day vulnerability in Gladinet CentreStack and Triofox products. Tracked as CVE-2025-11371, the unauthenticated Local File Inclusion (LFI) flaw allows…
Emerging from a recent wave of targeted campaigns, SnakeKeylogger has surfaced as a potent infostealer that capitalizes on PowerShell and social engineering. The malware’s operators…