Microsoft Teams Introduces Automatic Alerts for Malicious Links from Attackers
Microsoft to enhance security for its Teams platform by automatically warning users about malicious links in chat messages. The new feature, part of Microsoft Defender…
Microsoft to enhance security for its Teams platform by automatically warning users about malicious links in chat messages. The new feature, part of Microsoft Defender…
To ensure the security of sensitive internet data, it takes more than encryption; it requires clear principles, careful design, and evidential support. Naman Jain is…
In early May 2025, cybersecurity researchers began tracking a novel Remote Access Trojan (RAT) targeting Chinese-speaking users via phishing sites hosted on GitHub Pages. Masked…
Four Kenyan filmmakers became victims of sophisticated surveillance when FlexiSPY spyware was covertly installed on their devices while in police custody, according to forensic analysis…
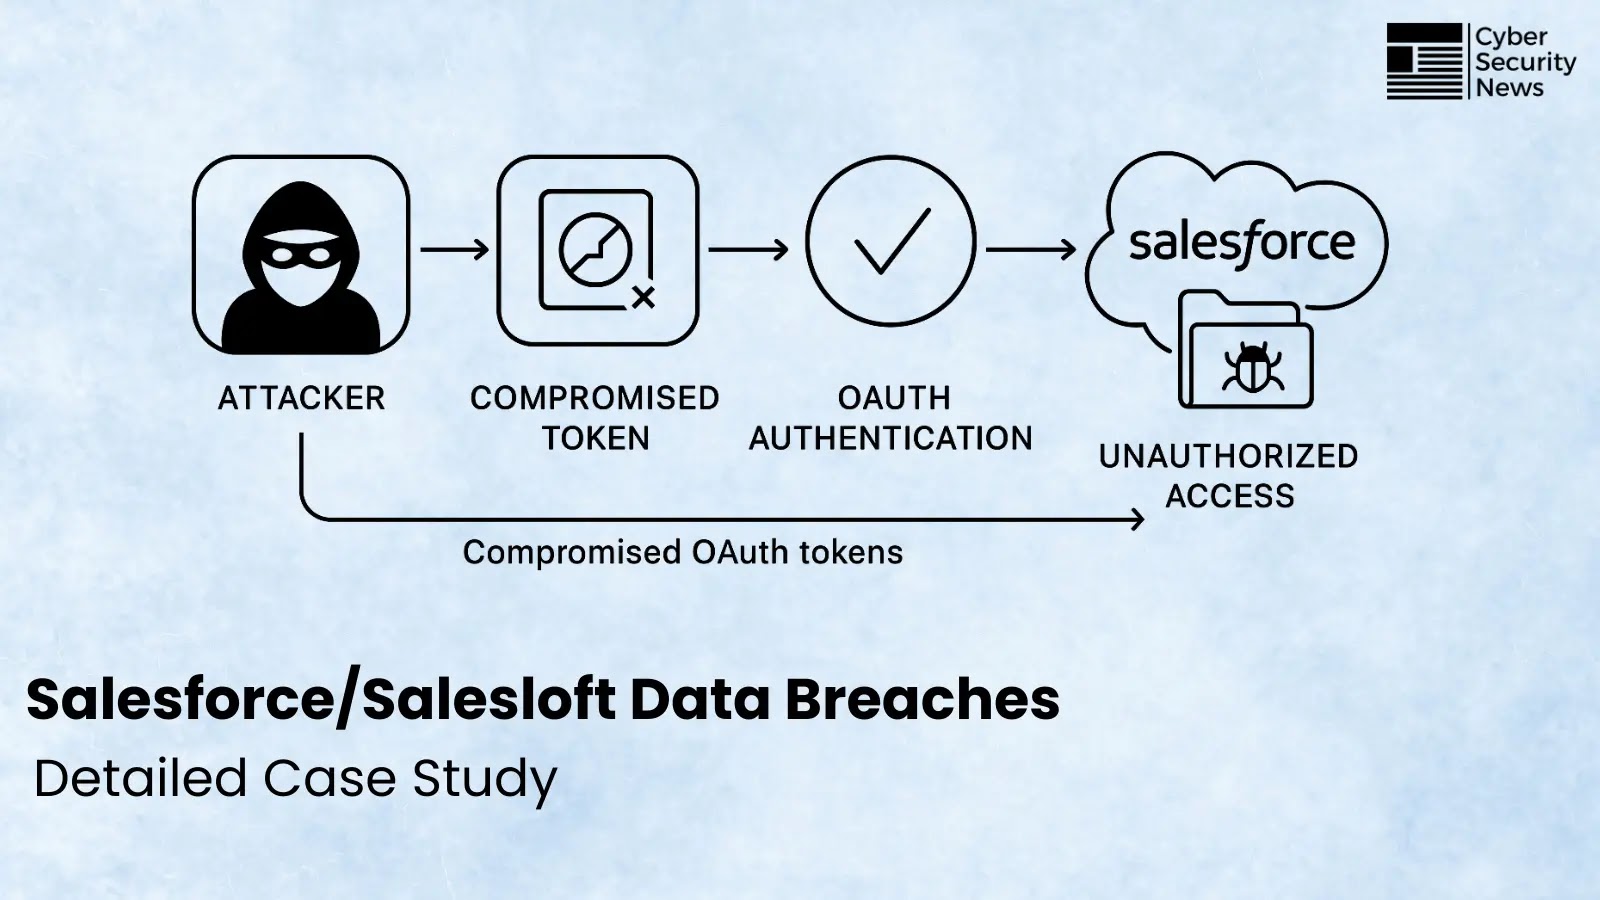
The Salesloft Drift data breaches of August 2025 stand as one of the most significant supply chain attacks in SaaS history, demonstrating how a single…
A novel speculative execution attack named VMSCAPE allows a malicious virtual machine (VM) to breach its security boundaries and steal sensitive data, like cryptographic keys,…
Cyber attackers constantly refine their evasion methods. That’s what makes threats, including phishing, increasingly hard to detect and investigate. Kits like Tycoon 2FA regularly evolve…
In early May 2025, security teams began observing a sudden rise in post-exploitation activity leveraging an open-source command-and-control framework known as AdaptixC2. Originally developed to…
In early March 2025, security teams first observed an unprecedented L7 DDoS botnet targeting web applications across multiple sectors. The botnet, rapidly expanding from an…
A previously unknown advanced persistent threat (APT) group has unleashed a new fileless malware framework, dubbed EggStreme, in a highly targeted espionage campaign against strategic…
Cornwell Quality Tools has disclosed a significant data breach that compromised the sensitive information of nearly 104,000 individuals. The incident involved unauthorized access to the…
ChillyHell first surfaced on public malware repositories in early May 2025, although its developer-signed notarization dates back to 2021. This modular backdoor has eluded detection…