Authorities Arrested Admins Of “LockerGoga,” “MegaCortex,” And “Nefilim” Ransomware Gands
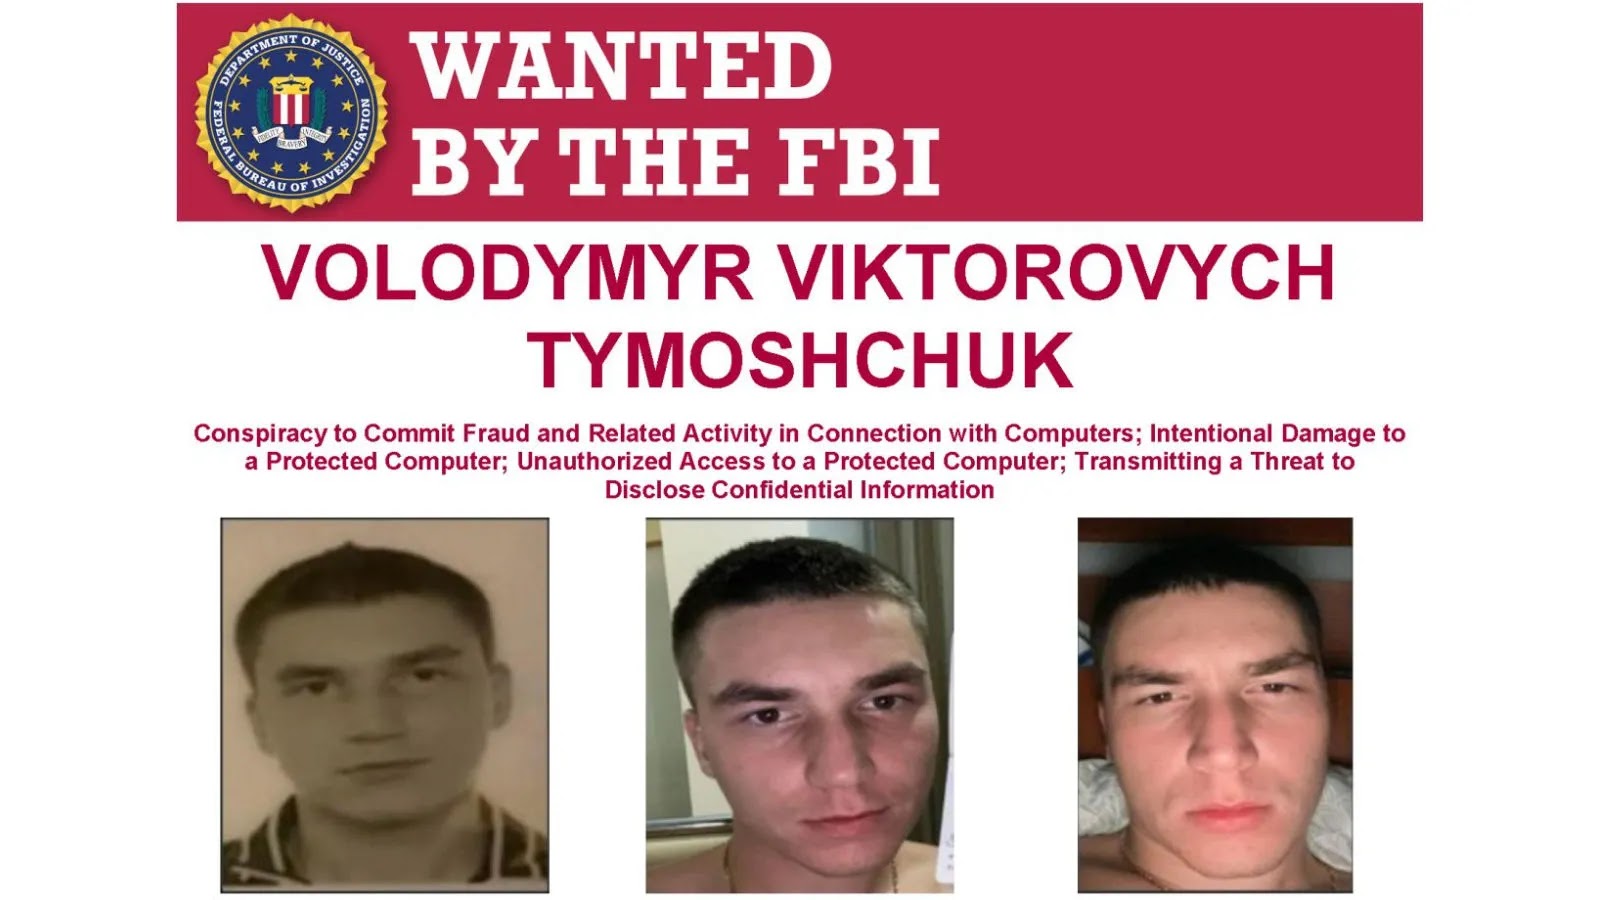
The U.S. District Court for the Eastern District of New York has unsealed a superseding indictment against a Ukrainian national, charging him with his alleged…
The U.S. District Court for the Eastern District of New York has unsealed a superseding indictment against a Ukrainian national, charging him with his alleged…
A sophisticated phishing campaign has emerged targeting Google Workspace organizations through fraudulent emails impersonating Google’s AppSheet platform. The attack demonstrates how cybercriminals exploit legitimate cloud…
A recent incident uncovered how a threat actor inadvertently exposed its entire operational workflow by installing a popular endpoint detection and response (EDR) agent on…
A critical security vulnerability has been discovered in the Amp’ed RF BT-AP 111 Bluetooth Access Point, exposing organizations to significant security risks through an unauthenticated…
Security researchers have recently observed a surge in sophisticated fileless malware campaigns targeting enterprise environments. AsyncRAT, a powerful Remote Access Trojan, leverages legitimate system tools…
CyberVolk ransomware first emerged in May 2024, rapidly evolving into a sophisticated threat aimed at government agencies and critical infrastructure in countries perceived as hostile…
A remote code execution vulnerability has been discovered in the Cursor AI Code Editor, enabling a malicious code repository to run code on a user’s…
Jaguar Land Rover (JLR) has confirmed that data was stolen during a major cyberattack that has crippled its global operations, bringing vehicle production to a…
Malicious actors have launched a sophisticated malvertising campaign on Facebook that coerces unsuspecting users into installing a fake “Meta Verified” browser extension. Promoted through seemingly…
Early this month, cybersecurity researchers uncovered a novel phishing campaign attributed to the Lazarus Group that targets developers and crypto professionals through a cleverly crafted…
In recent weeks, security teams have observed a sophisticated new strain of malware—dubbed GONEPOSTAL—that subverts Microsoft Outlook to relay command and control (C2) instructions. Emerging…
Security researchers have observed a sophisticated campaign in recent weeks targeting critical infrastructure and government entities across South Asia. Dubbed the DarkSamural operation, this attack…