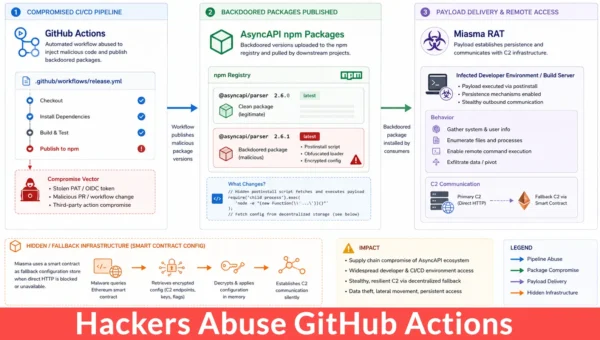
Hackers Abuse GitHub Actions to Backdoor AsyncAPI npm Packages With Miasma RAT
A supply chain attack has pushed Miasma malware into trusted AsyncAPI npm packages, putting developer systems and automated build environments at risk. Attackers used a…
A supply chain attack has pushed Miasma malware into trusted AsyncAPI npm packages, putting developer systems and automated build environments at risk. Attackers used a…
A ransomware campaign is now targeting the assets behind artificial intelligence systems. The threat actor known as JADEPUFFER has evolved from damaging databases to deploying…
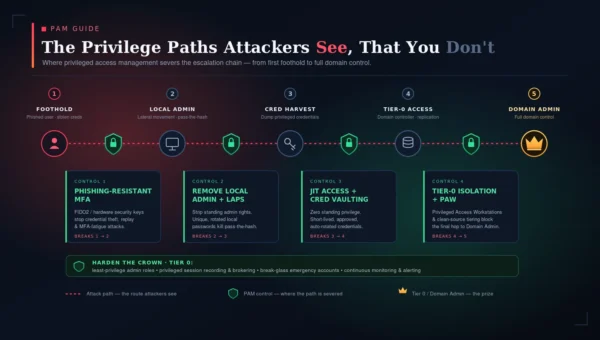
Why identity fragmentation is the blind spot behind most breaches—and what a platform approach changes The Identity Problem Hiding in Plain Sight Identity is at…
Critical wp2shell RCE Vulnerability – Complete Details Including PoC and Active Exploitation Overview A critical pre-authentication remote code execution (RCE) vulnerability chain nicknamed “wp2shell” has…
A stealthy new malware strain called HOLLOWGRAPH that hijacks Microsoft 365 calendars to secretly communicate with hackers, disguising malicious commands as ordinary calendar invites. HOLLOWGRAPH…
Windows defenders are facing a new way for attackers to hide activity after gaining administrator access. The technique abuses Windows bind links, a legitimate feature…
Microsoft SharePoint Server flaws are being actively exploited to gain remote code execution, install persistent web shells, and steal cryptographic keys from exposed systems. The…
A newly disclosed flaw tracked as CVE-2026-42533 affects nginx’s script engine and has been silently exploitable since March 2011, when the map directive gained regex…
This week’s cybersecurity situation shows a clear reality: every part of technology, from identity systems to common productivity tools, can be hacked or compromised. Microsoft’s…
A new open-source tool is bringing autonomous AI agents into offensive security workflows. PentestCode, a hard fork of OpenCode rebuilt specifically for penetration testing, runs…
A sharp structural shift has been identified in the botnet landscape. Security researchers at XLab have uncovered NadMesh, a Go-based botnet that has been spreading…
Ernst & Young LLP (EY) is notifying clients that an unauthorized third party breached a support ticket platform used by its IT staff, downloading documents…