Microsoft Details Scattered Spider TTPs Observed in Recent Attack Chains
In mid-2025, a new surge of targeted intrusions, attributed to the threat group known variously as Scattered Spider, Octo Tempest, UNC3944, Muddled Libra, and 0ktapus,…
In mid-2025, a new surge of targeted intrusions, attributed to the threat group known variously as Scattered Spider, Octo Tempest, UNC3944, Muddled Libra, and 0ktapus,…
CISA issued three significant Industrial Control Systems (ICS) advisories on July 17, 2025, addressing critical vulnerabilities affecting energy monitoring, healthcare imaging, and access control systems. …
A critical security vulnerability in TeleMessageTM SGNL, an enterprise messaging system modeled after Signal, has been actively exploited by cybercriminals seeking to extract sensitive user…
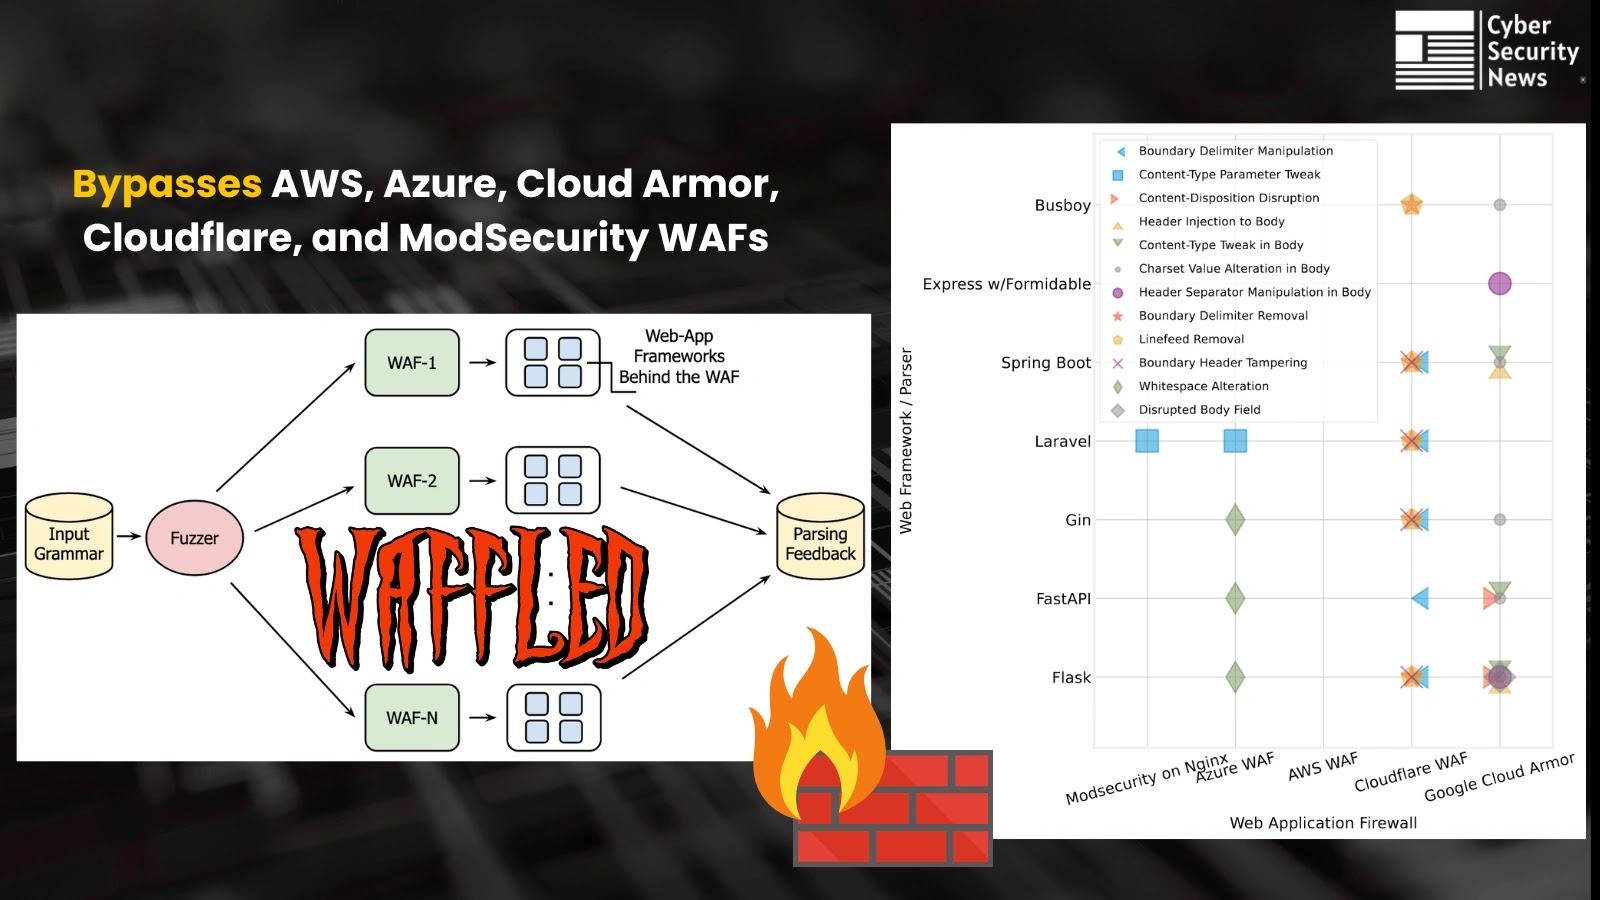
WAFFLED is a recently disclosed technique that evades leading Web Application Firewalls (WAFs) by targeting subtle parsing inconsistencies rather than tampering with the malicious payload…
Two critical vulnerabilities in the BIND 9 DNS resolver software are affecting organizations worldwide, with potential cache poisoning and denial-of-service attacks. The vulnerabilities, identified as…
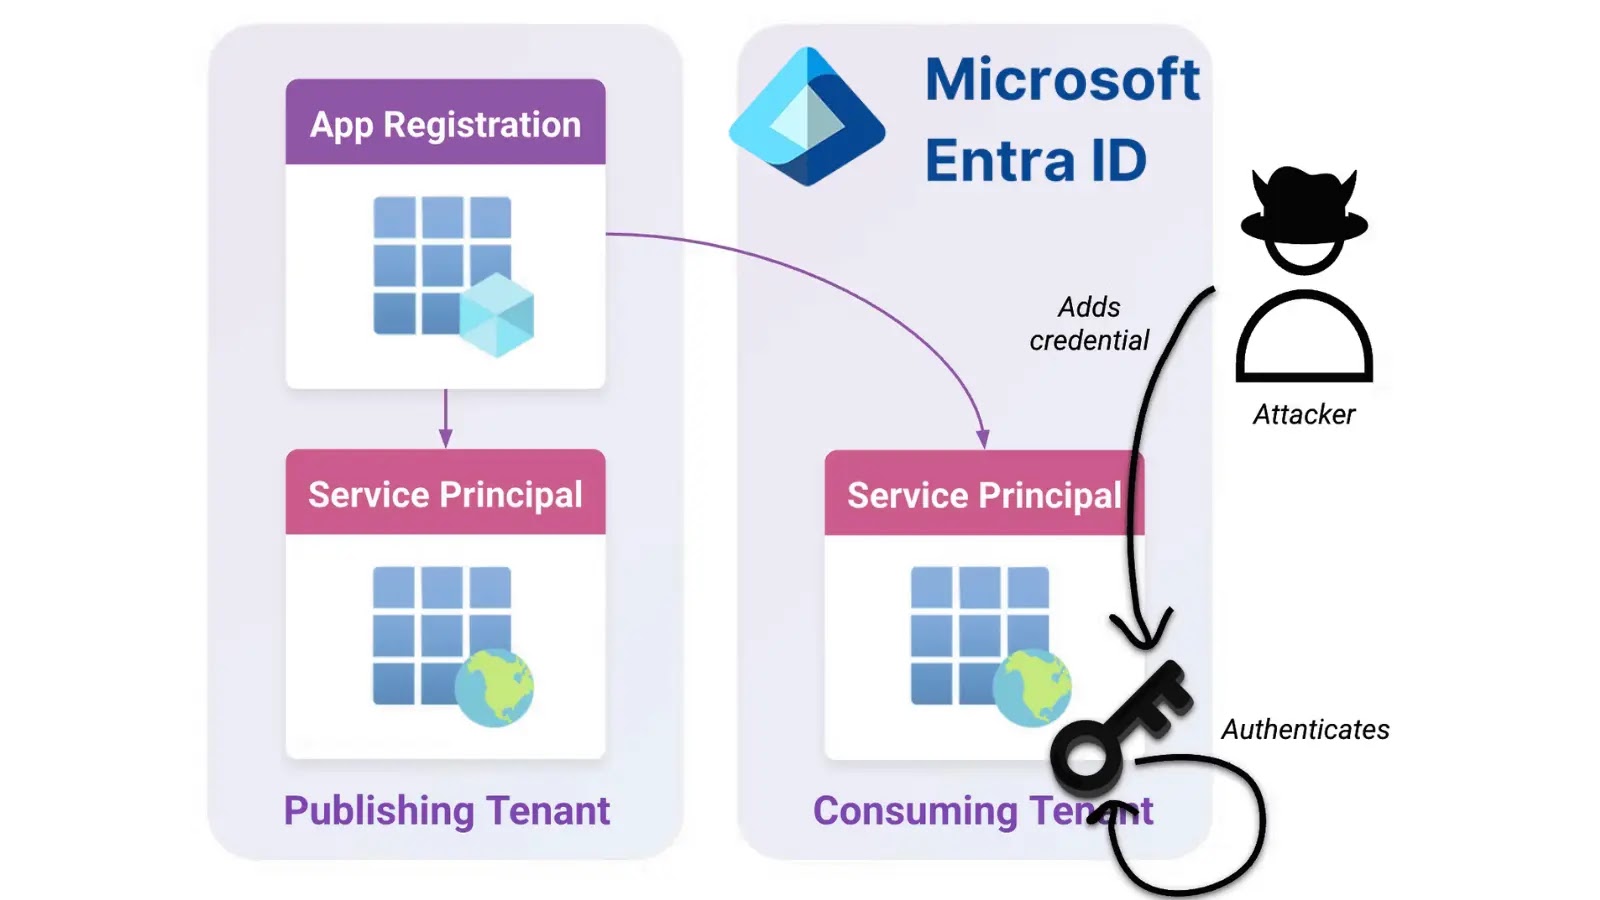
A critical vulnerability in Microsoft Entra ID allows attackers to escalate privileges to the Global Administrator role through the exploitation of first-party applications. The vulnerability,…
Last week, Ukraine’s Main Intelligence Directorate (GUR) orchestrated a sophisticated cyberattack against Gaskar Integration, a leading Russian drone manufacturer. The operation began with reconnaissance of…
A sophisticated Chinese state-sponsored cyber espionage campaign has emerged targeting Taiwan’s critical semiconductor industry, employing weaponized Cobalt Strike beacons and advanced social engineering tactics. Between…
A sophisticated new attack vector where malicious actors are hiding malware inside DNS records, exploiting a critical blind spot in most organizations’ security infrastructure. This…
The global hacktivist landscape has undergone a dramatic transformation since 2022, evolving from primarily ideologically motivated actors into a complex ecosystem where attention-seeking behavior and…
The H2Miner botnet, first observed in late 2019, has resurfaced with an expanded arsenal that blurs the line between cryptojacking and ransomware. The latest campaign…
Researchers have uncovered critical security vulnerabilities affecting millions of computer servers and routers worldwide, stemming from the insecure implementation of fundamental internet tunneling protocols. The…