What Is Cyber Threat Intelligence: Quick Guide For CISOs
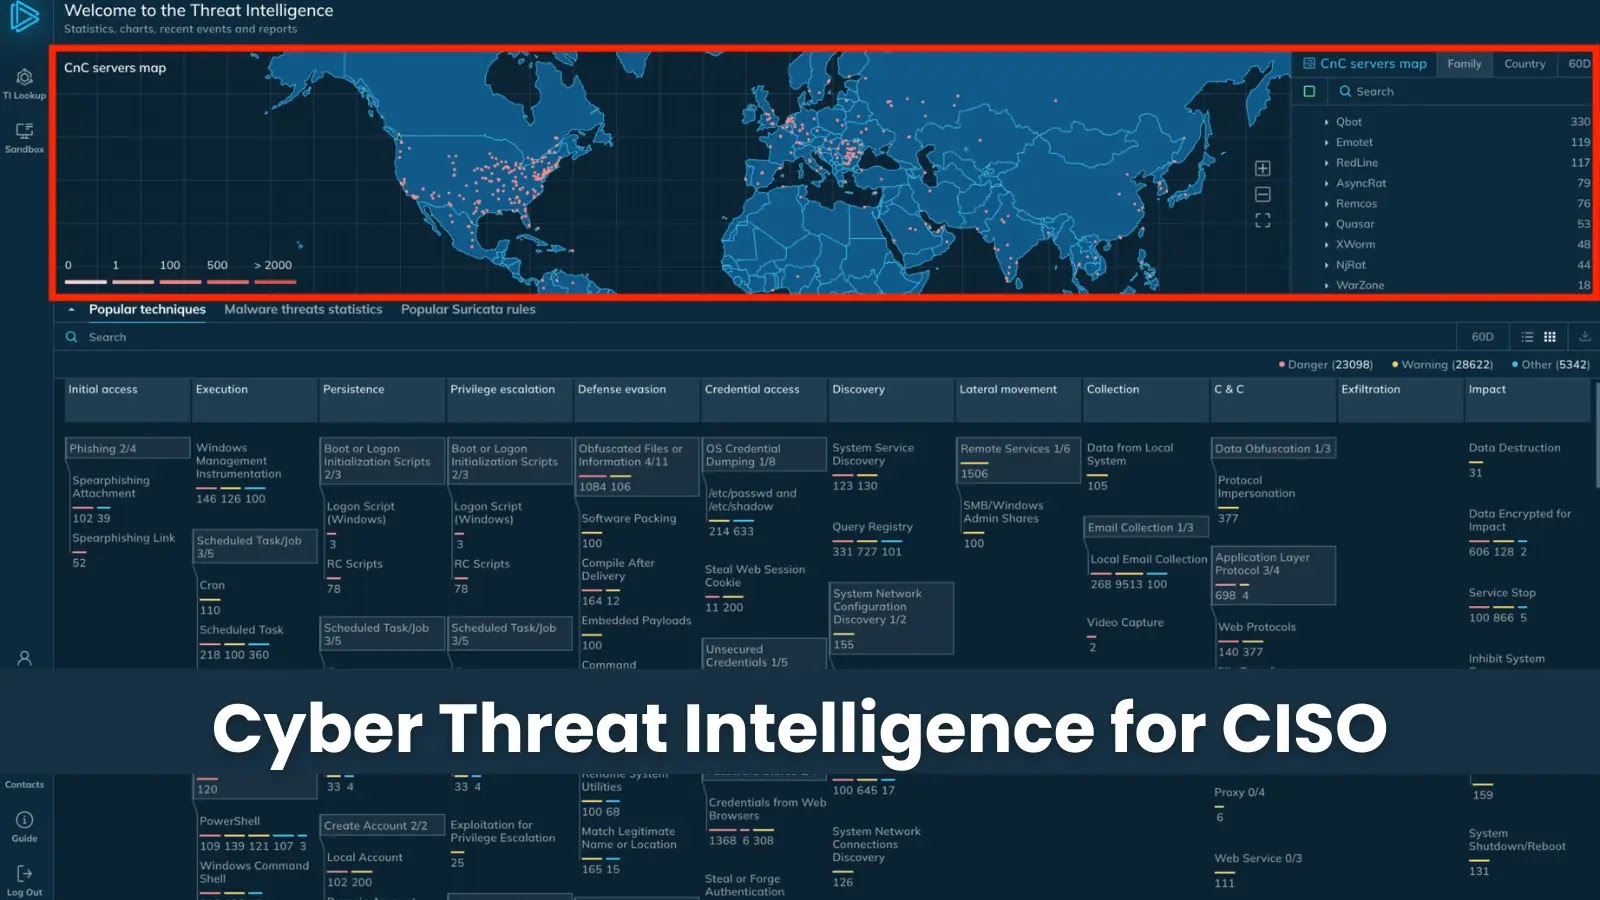
Cyber threat intelligence (CTI) is the practice of collecting, analyzing, and transforming data about cyber threats into actionable insights to protect organizations. For Chief Information…
Cyber threat intelligence (CTI) is the practice of collecting, analyzing, and transforming data about cyber threats into actionable insights to protect organizations. For Chief Information…
Aembit, the workload identity and access management (IAM) company, today announced a major expansion of its platform to support Microsoft environments. With this launch, enterprises…
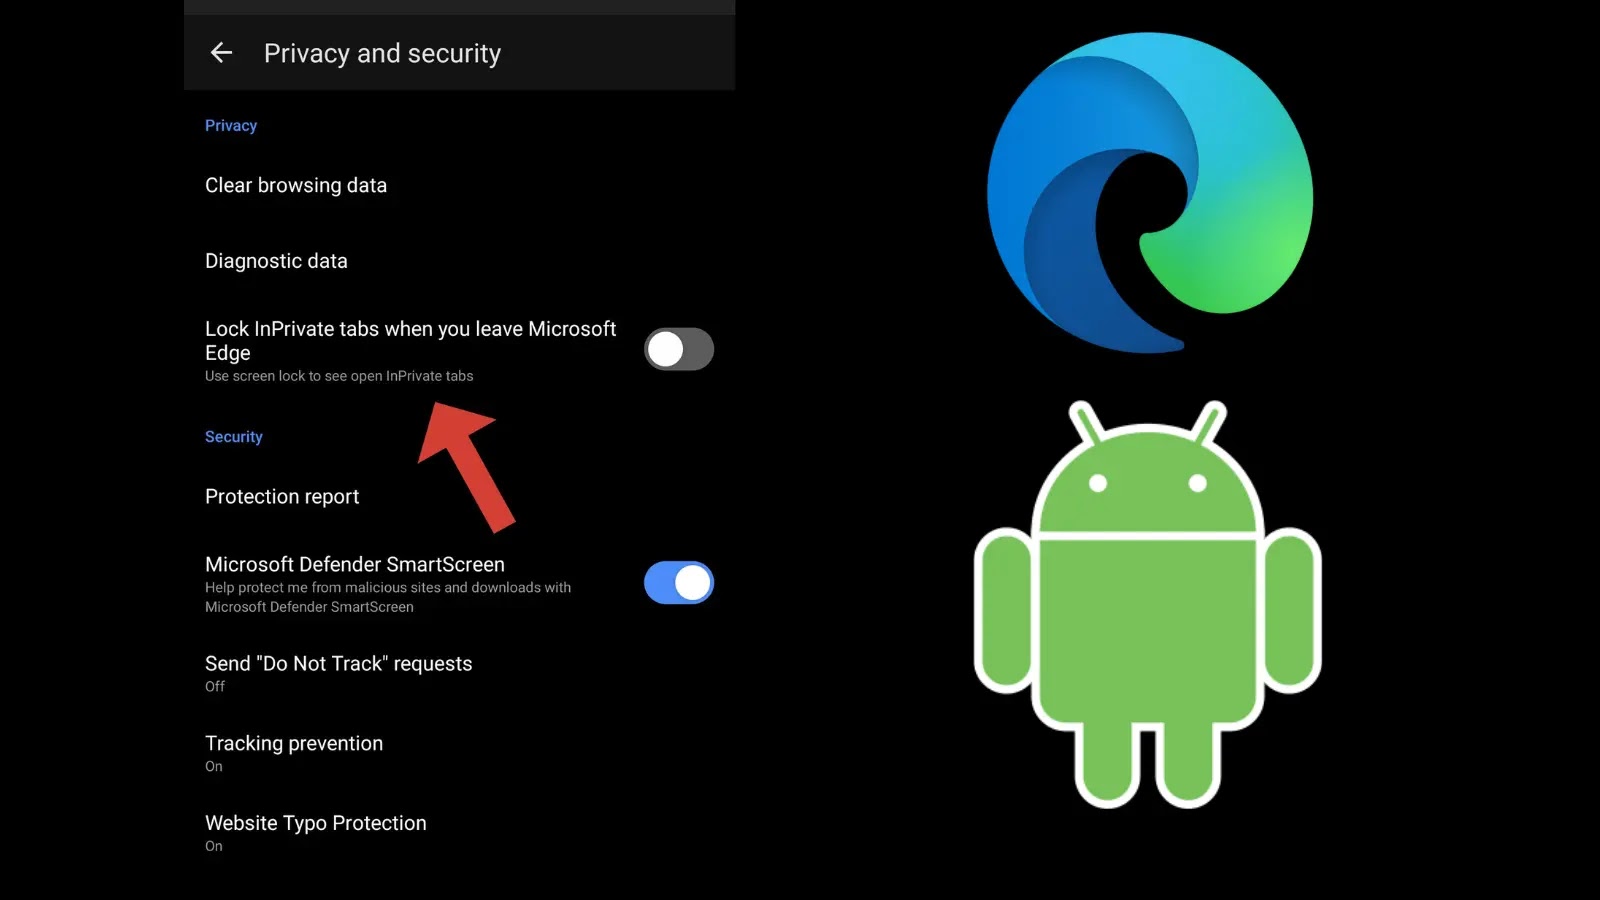
Microsoft Edge for Android is rolling out an enhanced privacy feature that allows users to secure their InPrivate browsing sessions with PIN codes or biometric…
A high-severity vulnerability was uncovered in Splunk Universal Forwarder for Windows that compromises directory access controls. The flaw, designated CVE-2025-20298 with a CVSSv3.1 score of…
A new cross-site scripting (XSS) vulnerability in Safari that exploits the browser’s TypeError exception handling mechanism to execute arbitrary JavaScript code. The flaw, discovered during…
Cybercriminals have launched a sophisticated campaign targeting travelers through fake Booking.com websites that deploy AsyncRAT malware, according to recent security research. The threat actors redirect…
A sophisticated cryptocurrency theft campaign has emerged on the npm package registry, targeting developers and cryptocurrency users through malicious packages designed to drain Ethereum and…
A significant vulnerability, CVE-2025-26396, affects the SolarWinds Dameware Mini Remote Control Service could allow attackers to escalate privileges on affected systems. Security researcher Alexander Pudwill,…
A significant denial of service vulnerability has been discovered in ModSecurity, one of the most widely deployed open-source web application firewall (WAF) engines used to…
Multiple security vulnerabilities in Hewlett-Packard Enterprise (HPE) StoreOnce software platform that could allow remote attackers to execute malicious code, bypass authentication mechanisms, and access sensitive…
A significant security vulnerability in the Splunk Enterprise platform could allow low-privileged attackers to execute unauthorized JavaScript code through a reflected Cross-Site Scripting (XSS) flaw. …
Cybercriminals are increasingly leveraging misconfigured artificial intelligence tools to execute sophisticated attacks that generate and deploy malicious payloads automatically, marking a concerning evolution in threat…