Facebook Awarded $100,000 for Bug that Allows Internal Access to Server
Facebook has awarded a $100,000 bug bounty to security researcher Ben Sadeghipour for discovering a critical vulnerability in the company’s ad platform. The flaw, identified…
Facebook has awarded a $100,000 bug bounty to security researcher Ben Sadeghipour for discovering a critical vulnerability in the company’s ad platform. The flaw, identified…
Proton Mail, the renowned privacy-focused email service, experienced a significant global outage today, leaving users worldwide unable to access their email accounts. The disruption began…
The NonEuclid Remote Access Trojan (RAT), a highly sophisticated malware, has been detected, allowing unauthorized remote access via advanced evasion techniques and ransomware encryption of…
Imagine an employee receiving an email that looks completely legitimate, maybe it’s a fake invoice or a shipping update. They click on the attachment, and…
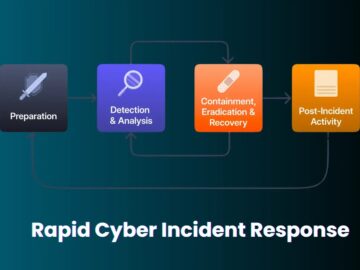
As you probably know by now, it doesn’t really matter how big in size your business is, you’re going to be up against the risk…
The researchers exploited a novel attack vector by hijacking abandoned backdoors within other backdoors, which relied on expired or abandoned infrastructure, such as expired domains.…
The Green Bay Packers organization has disclosed a data breach affecting thousands of customers who made purchases on their official online store, packersproshop. The incident,…
Attackers have evolved a sophisticated social engineering scheme to target Middle Eastern banking consumers by posing as government officials and utilizing remote access software to…
A critical vulnerability in Kerio Control, a popular firewall and Unified Threat Management (UTM) product, has been discovered that could allow attackers to execute remote…
A proof-of-concept (PoC) exploit for the critical Apache Struts vulnerability, CVE-2024-53677, has been publicly released, raising alarm across the cybersecurity community. This vulnerability, which scores…
A proof-of-concept (PoC) exploit code for a critical vulnerability in macOS, identified as CVE-2024-54527 has been disclosed. This vulnerability allows attackers to bypass the Transparency,…
Multiple vulnerabilities in Palo Alto Networks’ Expedition migration tool have been discovered, potentially exposing sensitive firewall credentials, including usernames, cleartext passwords, device configurations, and API…