Popular Go Library fsnotify Raises Supply Chain Alarms After Maintainer Access Changes
A widely used Go library called fsnotify has found itself at the center of a supply chain security scare after a sudden change in maintainer…
A widely used Go library called fsnotify has found itself at the center of a supply chain security scare after a sudden change in maintainer…
The infamous hacking group ShinyHunters has struck again, this time targeting Instructure, the company behind Canvas Learning Management System (LMS). In early May 2026, Instructure…
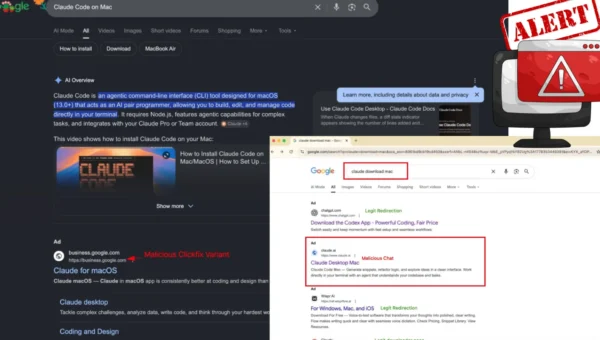
Threat actors are executing a sophisticated malvertising campaign targeting macOS users via poisoned Google Ads and deceptive artificial intelligence applications. Researchers recently uncovered an operation…
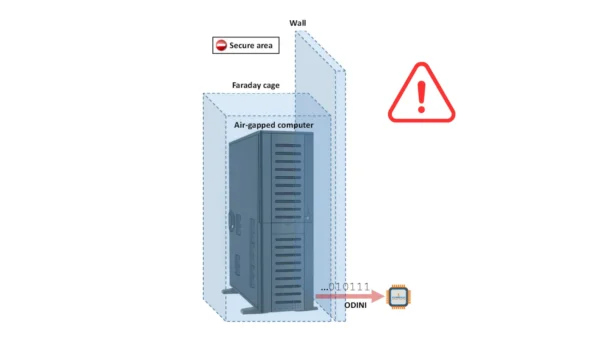
ODINI is a sophisticated proof-of-concept malware capable of extracting sensitive information from air-gapped computers protected by Faraday cages. By modulating the targeted computer’s CPU workload…
A dangerous new infostealer campaign is targeting some of the most sensitive data people store on their computers. Disguised as a legitimate installer for OpenClaw,…
Škoda Auto has disclosed a significant IT security incident affecting its official online shop, revealing that unauthorized individuals exploited a vulnerability in the platform’s standard…
Microsoft has disclosed and fully remediated three critical information disclosure vulnerabilities affecting Microsoft 365 Copilot and Copilot Chat in Microsoft Edge, all released on May…
Let’s Encrypt temporarily suspended all certificate issuance on May 8, 2026, after engineers identified a critical issue involving a cross-signed certificate linking the organization’s Generation…
A data breach at GFN.AM, an authorized NVIDIA GeForce NOW cloud gaming service provider operating under “GFN CLOUD INTERNET SERVICES” LLC, has exposed personal information…
A highly sophisticated Brazilian banking trojan named TCLBANKER, tracked under the campaign REF3076, this malware represents a major update to the older Maverick and SORVEPOTEL…
A newly identified malware campaign is targeting senior executives and government investigators across Southeast Asia, using a modular Remote Access Trojan capable of stealing credentials,…
A new backdoor called PamDOORa has emerged as a serious and growing threat to Linux systems, targeting one of the most trusted components of the…