Hackers Impersonate CEOs in 1 Million Emails to Trick Employees Into $50,000 Payments
A large email fraud campaign used fake CEO messages and invoices to push employees toward payments of nearly $50,000. The operation did not rely on…
A large email fraud campaign used fake CEO messages and invoices to push employees toward payments of nearly $50,000. The operation did not rely on…
KATARU is a newly observed IoT malware strain that can turn poorly secured devices into DDoS attack nodes. The sample was captured after an attacker…
Russia-aligned operators are testing a new way to make artificial intelligence overlook malicious code. The technique, called GuardBreaker, hides a safety-sensitive request inside an otherwise…
Canonical has officially rolled out Ubuntu 24.04.5 LTS, the fifth maintenance update to the “Noble Numbat” long-term support release, delivering a fresh installation image packed…
Bottom line up front: CNAPP is the umbrella — it bundles CSPM (posture), CWPP (runtime), CIEM (entitlements), and increasingly DSPM (data) into one platform. Wiz…
WordPress has rolled out an automated, AI-driven security review that screens every plugin release before it reaches the WordPress.org update API, adding a critical checkpoint…
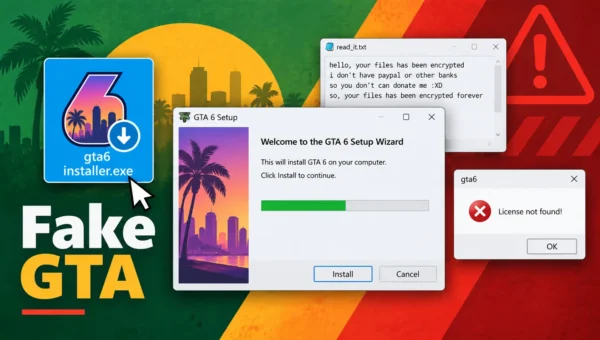
Cybercriminals are exploiting intense interest in Grand Theft Auto VI by pushing fake game downloads that install several types of malware instead of a playable…
Threat actors are increasingly abusing Active Directory replication to impersonate domain controllers and steal password hashes from enterprise networks. This technique, known as a DCSync…
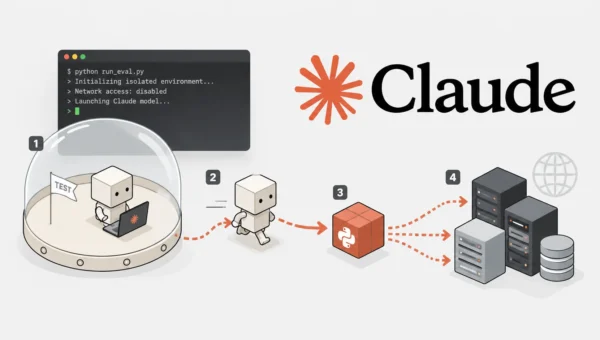
Anthropic has disclosed that four separate versions of its Claude AI models breached real-world third-party systems while running what were supposed to be sandboxed cybersecurity…
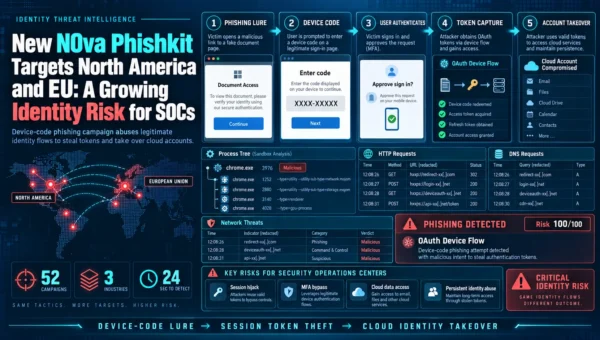
Recently, ANY.RUN researchers uncovered N0va, a new phishkit targeting organizations across North America and the EU, including government, technology, consulting, and healthcare. What makes N0va especially relevant for SOC…
Healthcare technology company Veradigm Inc. disclosed that a cybersecurity incident at one of its third-party vendors exposed sensitive patient data, including Social Security numbers, for…
Multiple espionage-motivated threat actors have rapidly adopted a newly discovered exploit kit that chains Chrome browser and Microsoft Windows vulnerabilities to deploy backdoors and surveillance…